Eliminate Security Blind Spots with Armis Integrations
Overview
Armis Centrix provides continuous, agentless visibility and exposure management across IT, OT, IoT, IoMT, and cloud assets. By integrating Armis with your security and IT ecosystem, we help enrich asset context, improve visibility, and automate threat response across enterprise environments.
Key Products
Armis Centrix for Asset Management and Security (CAASM)
Delivers 100% continuous visibility and an accurate inventory of every connected asset managed, unmanaged, IT, OT, or IoT without installing agents.
Armis Centrix for Vulnerability Prioritization and Remediation (VIPR)
Closes the gap between finding and fixing risk by combining evidence-based vulnerability validation with threat intelligence to prioritize critical exposures.
Armis Centrix for OT/IoT Security
Safeguards cyber-physical systems and operational technology through passive monitoring, deep protocol inspection, and automated risk scoring.
Armis Centrix for Medical Device Security
Protects connected healthcare infrastructure and clinical IoMT devices, ensuring continuous patient safety and regulatory compliance.
Armis Centrix for Application Security
Extends exposure management into application pipelines, detecting software vulnerabilities and misconfigurations across enterprise codebases.
Armis Centrix for Early Warning
Uses AI-driven threat intelligence to monitor dark web activity and emerging exploits, alerting teams months before threats reach public disclosure.
Armis Integration Architecture
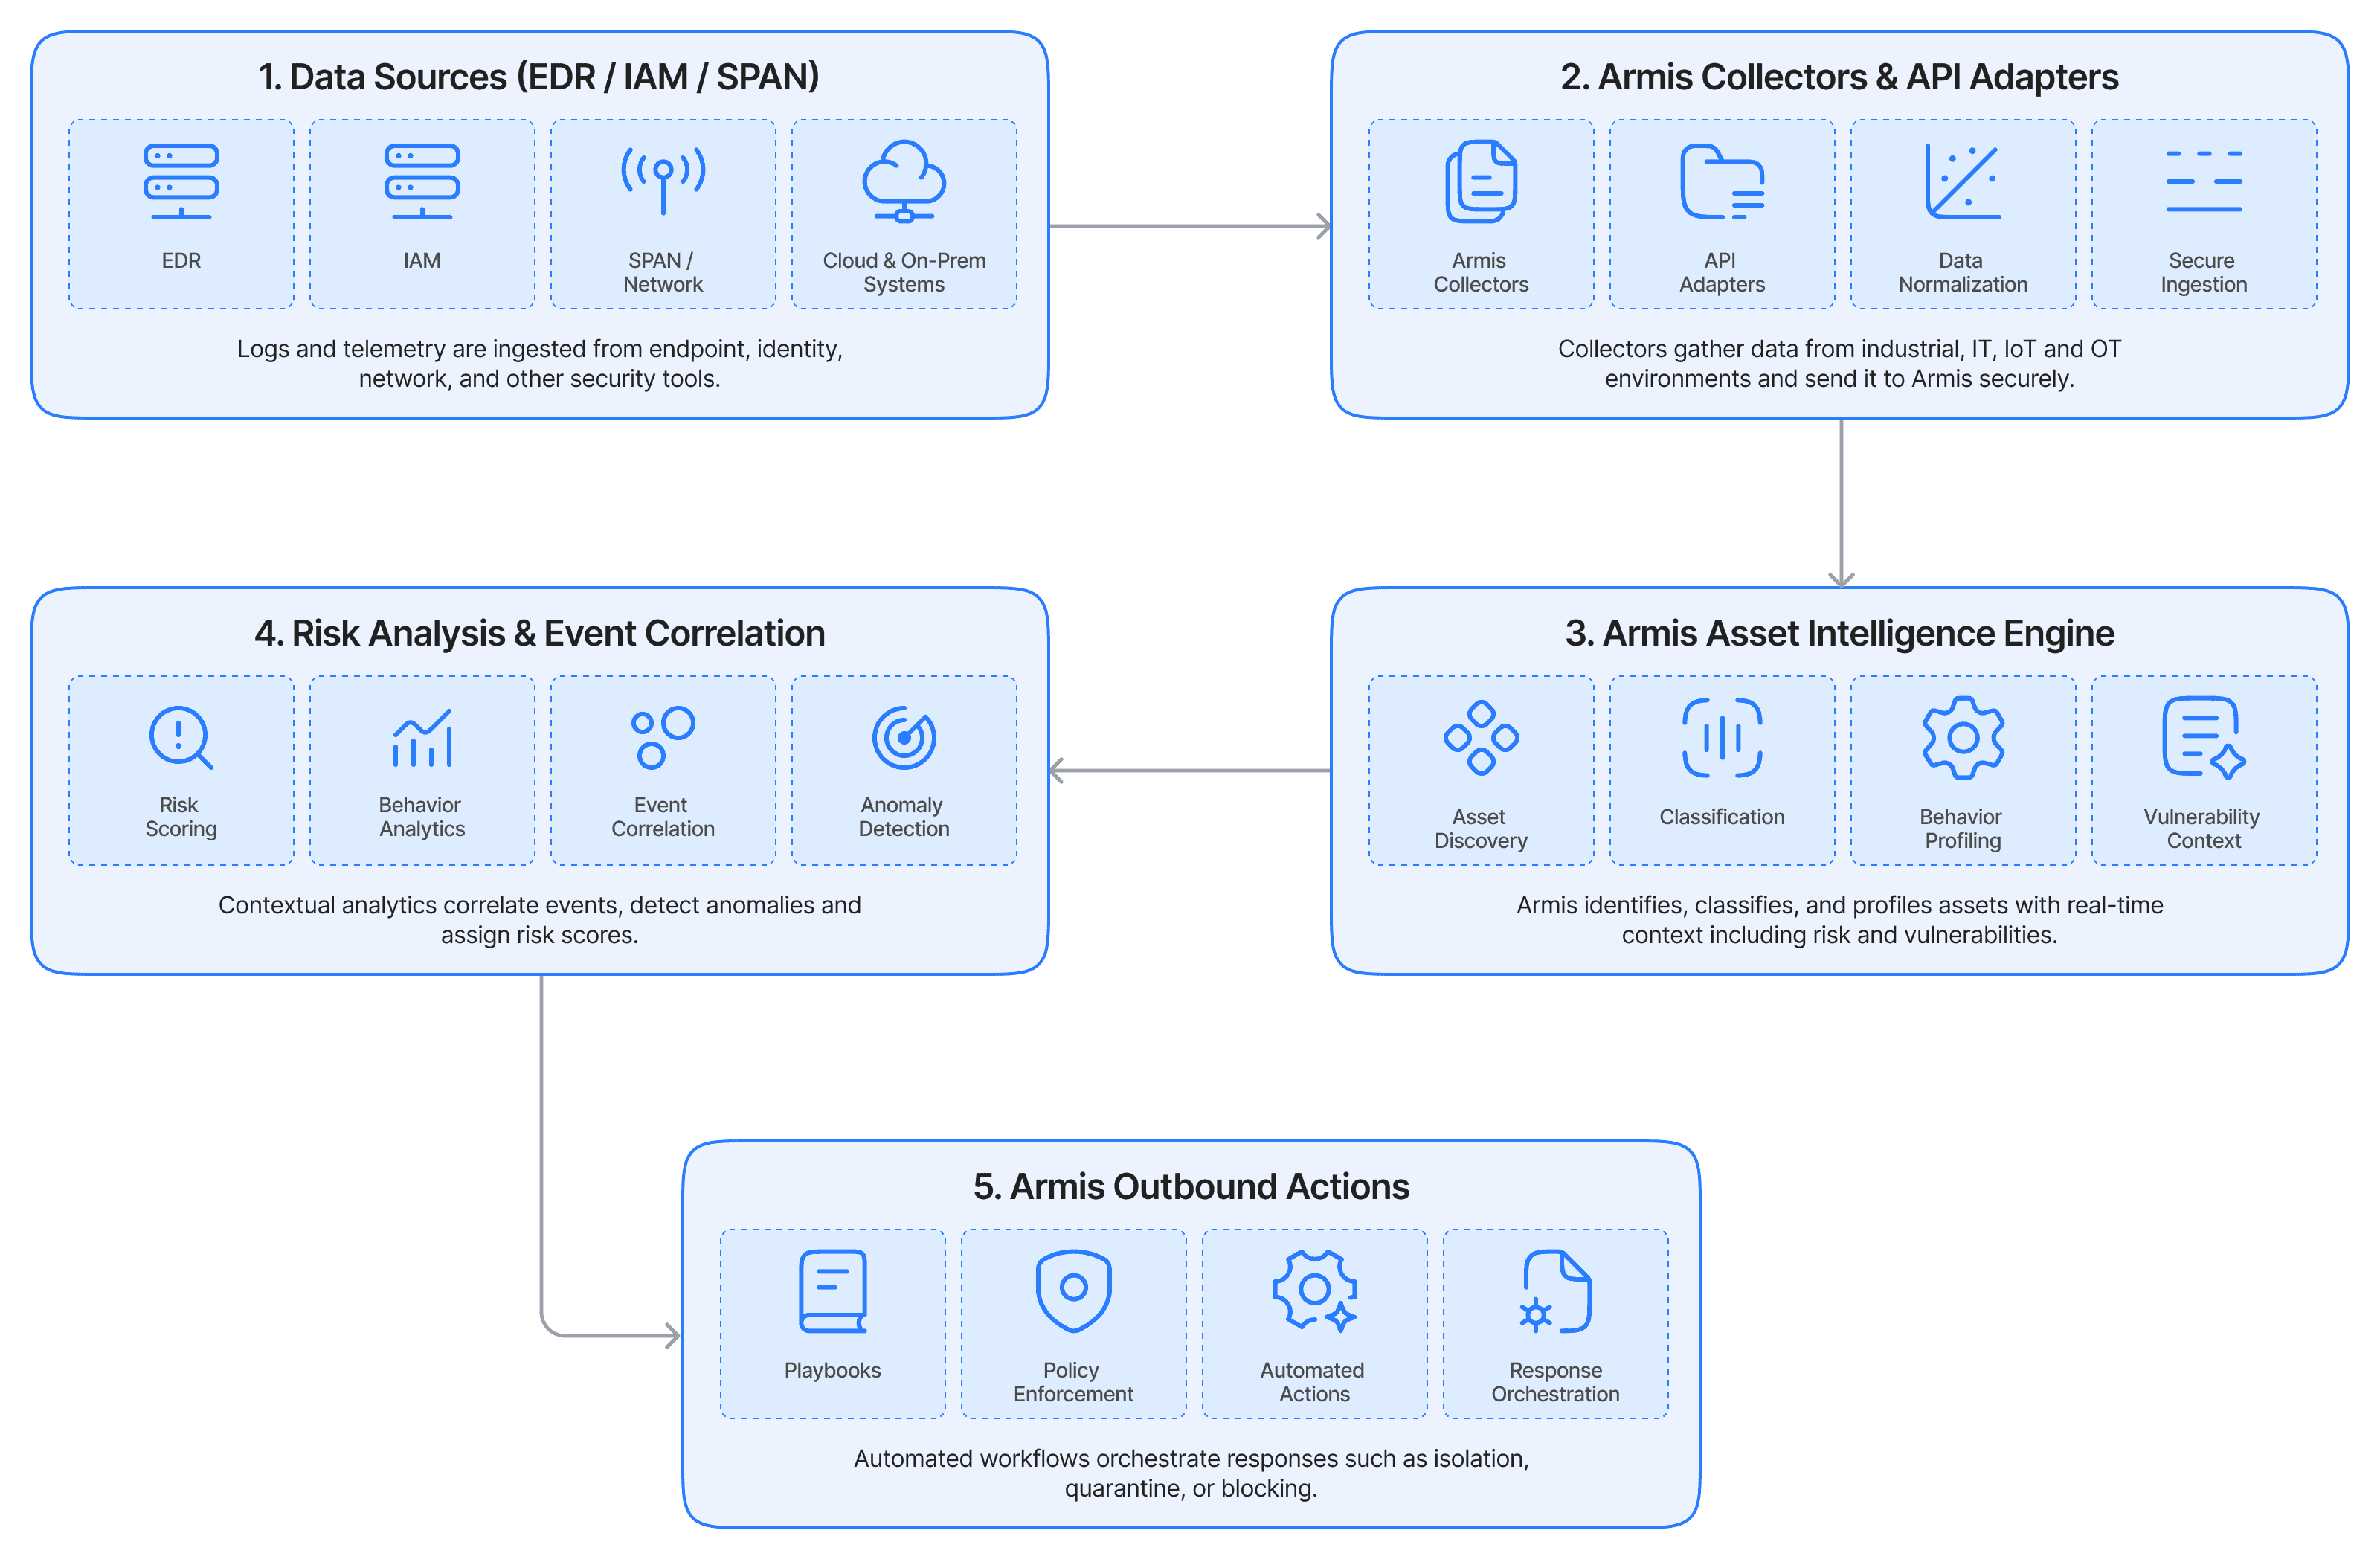
External IT and security tools (such as EDRs, identity providers, and vulnerability scanners) push environment telemetry into Armis, while Armis passively monitors network traffic. Armis correlates these inputs against its global Asset Intelligence Engine to discover unmanaged assets, detect anomalous behavior, and compute risk scores. Armis then feeds enriched asset context and validated alerts back into CMDBs, SIEMs, ticketing systems, and network enforcement controls for automated response.
Streamlined Logic
1. Ingest & Discover: API adapters fetch active asset data from EDRs (e.g., CrowdStrike) and identity management platforms (e.g., Active Directory), while Armis collectors capture passive network traffic.
2. Correlate & Classify: The Armis Asset Intelligence Engine analyzes telemetry across over 6.5 billion asset profiles, accurately classifying device type, OS, vulnerabilities, and baseline behavior.
3. Identify & Prioritize Risk: Armis detects unmanaged endpoints, misconfigurations, policy violations, and suspicious behavior, assigning a dynamic risk score to each asset.
4. Enrich & Sync: Armis synchronizes high-confidence asset profiles to your ITAM/CMDB (e.g., ServiceNow) to eliminate stale records and fill blind spots.
5. Orchestrate & Remediate: When risk crosses a critical threshold, Armis automatically generates tickets in Jira/ServiceNow or sends enforcement commands to your NAC/firewall to isolate the asset.
Armis Integration Benefits
Out-of-the-Box API Adapters
Ingest asset metadata, user identity, and security telemetry from existing management platforms (EDR, CMDB, IAM, and MDM) to continuously update device risk scores.
Passive Collector & Traffic Ingestion
Deploys virtual or physical collectors on-premises or in cloud environments to passively process SPAN/TAP network traffic without adding overhead or interrupting operations.
Bi-Directional Enforcement & SOAR Actions
Pushes real-time alerts and risk scores into NACs, firewalls, and SOAR tools to automatically quarantine infected devices, update firewall rules, or block unauthorized access.
REST API & Webhooks Engine
Leverages Armis open REST APIs and webhooks to query the Asset Intelligence Engine, export custom reports, and build tailored automated workflows for unique enterprise needs.
Integration Use Cases
Accelerated Incident Response via SIEM & SOAR
Feed real-time alert context and detailed asset intelligence directly into your SIEM and SOAR tools to cut investigation times and automate threat containment protocols.
Closed-Loop Vulnerability Ticketing
Automatically trigger and assign ITSM tickets based on validated vulnerability risk scores and true asset ownership, ensuring security and operations teams address critical exposures faster.
Zero Trust Enforcement at the Network Edge
Connect Armis threat intelligence with network access controls and firewalls to automatically quarantine unmanaged or compromised endpoints the instant they breach security policies.
Similar Connectors