Unify Asset Visibility and Security with Forescout
Key Products
Universal Zero Trust Network Access (ZTNA)
Continuous posture evaluation and identity-aware access control to enforce least-privilege policies across hybrid networks.

OT & ICS Security
Deep industrial asset monitoring, protocol analysis, and threat detection designed specifically for operational technology environments.

Vistaro Platform & Core Security
Continuous, agentless asset discovery, classification, and access control across all connected devices, managed and unmanaged.
Forescout Integration Architecture
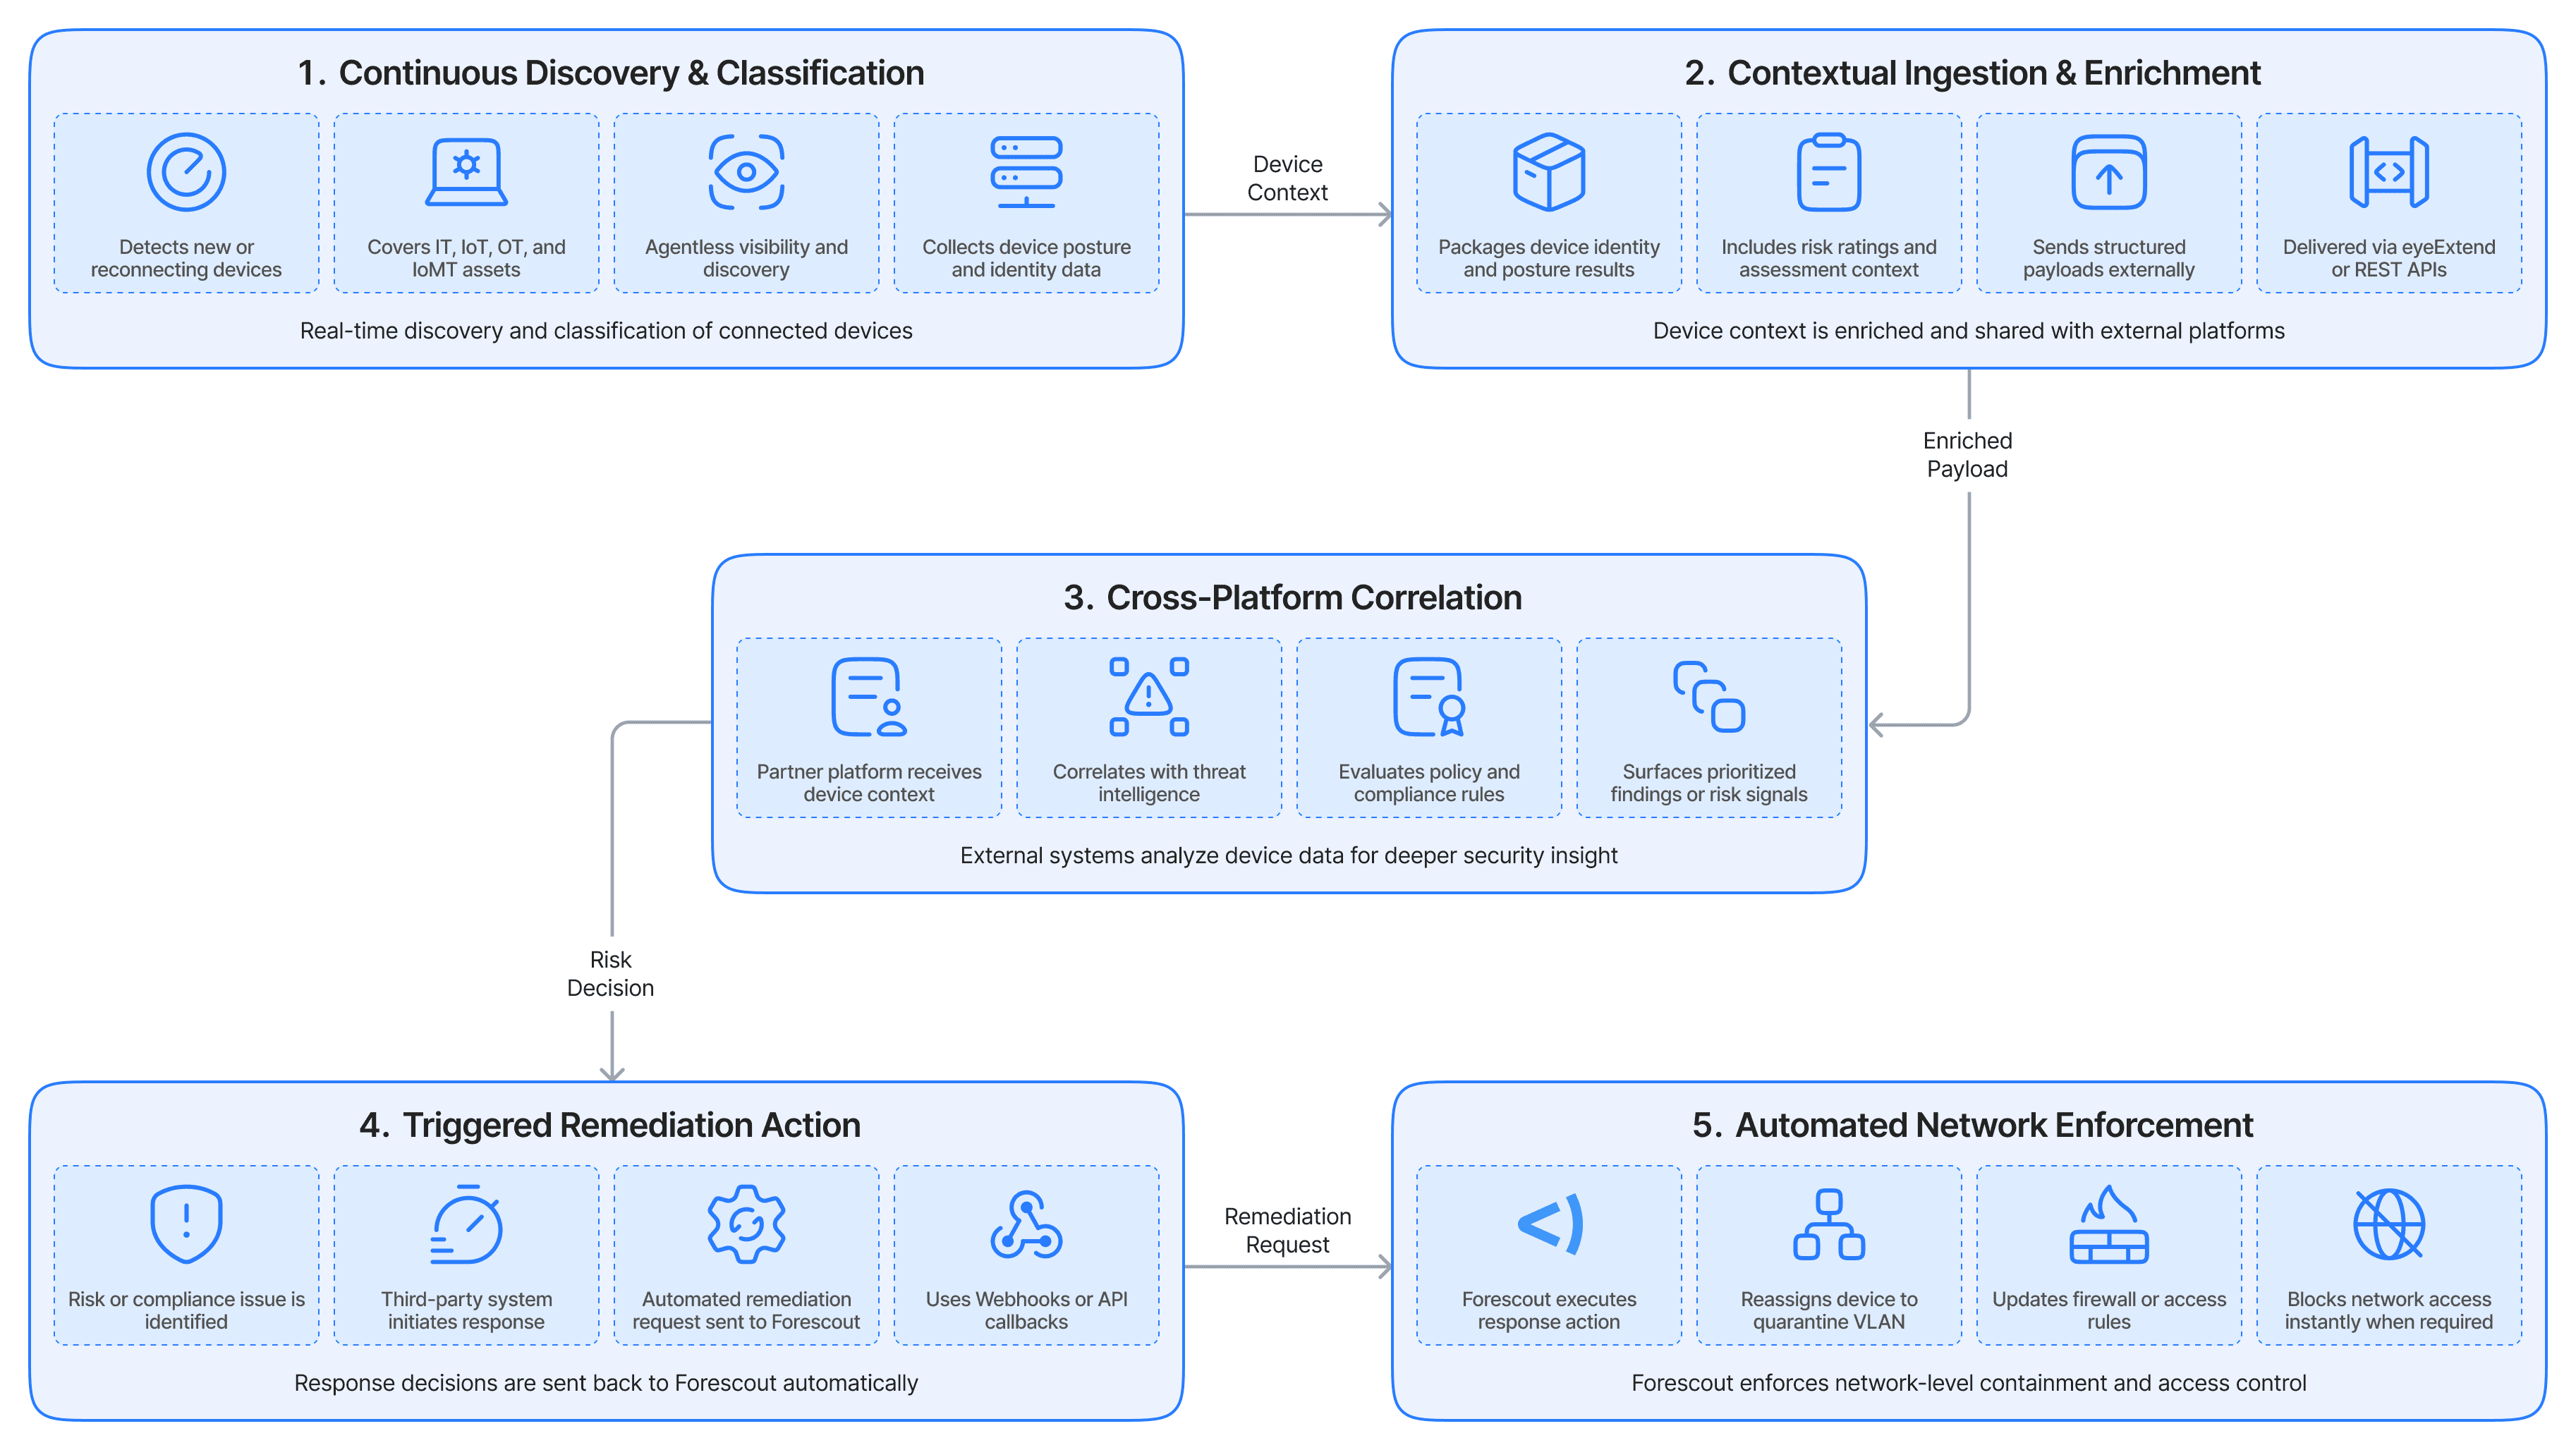
Forescout connects with external security and IT platforms to share real-time device intelligence, asset details, and vulnerability data. Through integrations with SIEM, EDR, and ITSM tools, teams can automate threat response, enforce network access policies, and remediate risks across their environments.
Architecture
1. Continuous Discovery & Classification: Forescout detects a new or reconnecting device (IT, IoT, OT, or IoMT) on the network and gathers deep posture data agentlessly.
2. Contextual Ingestion & Enrichment: Forescout packages device identity, posture assessment results, and risk ratings, sending structured payloads to an external system (e.g., SIEM or CMDB) via eyeExtend or REST APIs.
3. Cross-Platform Correlation: The integrated partner platform (e.g., EDR or SIEM) analyzes the incoming device context alongside external threat intelligence or policy rules.
4. Triggered Remediation Action: If a risk or compliance violation is identified, the third-party system sends an automated remediation request back into Forescout via the Forescout Web API / Connect API.
5. Automated Network Enforcement: Forescout executes the response action on the network layer, re-assigning the device to a quarantine VLAN, updating firewall rules, or blocking access instantly.
Forescout Integration Benefits
Pre-Built eyeExtend Modules
Packaged enterprise connectors designed for instant integration with leading tools such as ServiceNow, CrowdStrike, Microsoft, Splunk, and Palo Alto Networks.
eyeExtend Connect Apps
A lightweight, developer-friendly framework that enables rapid custom integration development using open REST APIs, Webhooks, and community-driven connector templates.
Open REST APIs
Bi-directional programmatic interfaces that allow external systems to query Forescout asset inventories, trigger posture assessments, or send remote remediation commands.
Syslog & Webhook Ingest/Export
Real-time event streaming using standard network protocols (TCP/UDP Syslog, HTTP POST) to send device state changes and security events to SIEMs or data lakes.
Integration Use Cases
Real-Time CMDB Sync & Asset Intelligence
Automatically populate and update enterprise ITSM platforms (such as ServiceNow) with deep, agentless asset telemetry. We ensure your CMDB accurately reflects unmanaged IoT/OT devices, OS builds, dynamic IP assignments, and network locations without manual entry or data drift.
Centralized Security Contextualization
We optimise threat triage by routing live alerts and threat intelligence to a single operational centre. Analysts can track malware detections, network events, and EDR telemetry alongside machine data without switching tabs.
Bi-Directional Vulnerability Management
Enhance security scanners (like Tenable, Rapid7, or Qualys) by feeding them real-time device connection triggers. Forescout notifies scanners the moment an unknown device hits the network, and ingests vulnerability scores back into Forescout to restrict high-risk devices until patched.
Similar Connectors