Transform Security and IT with Splunk
Key Products
Splunk Enterprise
Provides powerful data analytics capabilities, enabling organizations to search, monitor, and analyze machine-generated data for real-time insights and operational intelligence.
Splunk Cloud Platform
Delivers the features of Splunk Enterprise as a cloud-based service, offering scalability and flexibility for organizations using cloud infrastructure for data analytics.
Splunk Enterprise Security
Offers advanced security information and event management (SIEM) capabilities, helping organizations detect, investigate, and respond to security threats effectively.
Splunk SOAR
Automates security operations by orchestrating workflows and integrating various security tools, enabling faster and more efficient incident response.
Splunk Observability Cloud
Provides full-stack observability solutions, including infrastructure monitoring, application performance monitoring, and real user monitoring, ensuring reliability of digital systems.
Splunk IT Service Intelligence (ITSI)
Delivers insights into IT operations by correlating data across systems, providing a comprehensive view of service health, and facilitating proactive issue resolution.
Splunk Integrations
Splunk + ServiceNow: Integrating Splunk with ServiceNow automates incident creation from custom alert actions. This enables security teams to leverage Splunk's SIEM capabilities to detect anomalies and automatically generate incidents in ServiceNow, streamlining the incident management process.
Splunk + Operational Technology (OT) & Internet of Things (IoT) Security: By integrating Splunk with OT and IoT security applications, organizations can centralize monitoring of asset events. This integration involves configuring modular inputs with IoT API credentials, allowing Splunk to periodically poll IoT servers via REST API calls to fetch asset data. This approach enhances visibility into industrial environments and strengthens security postures.
Splunk + NVD-CVE Fetcher App: The NVD-CVE Fetcher App is a Splunk add-on that helps organizations stay updated with known vulnerabilities. By integrating this app, Splunk can automatically fetch and update the latest Common Vulnerabilities and Exposures (CVEs), enabling proactive vulnerability management and risk mitigation.
Splunk + Middleware Connectors: In scenarios where direct integration between security products is not feasible due to a lack of application frameworks, middleware connectors can bridge the gap. These connectors facilitate communication between APIs, enabling seamless data exchange and integration between Splunk and other security applications.
Splunk Architecture
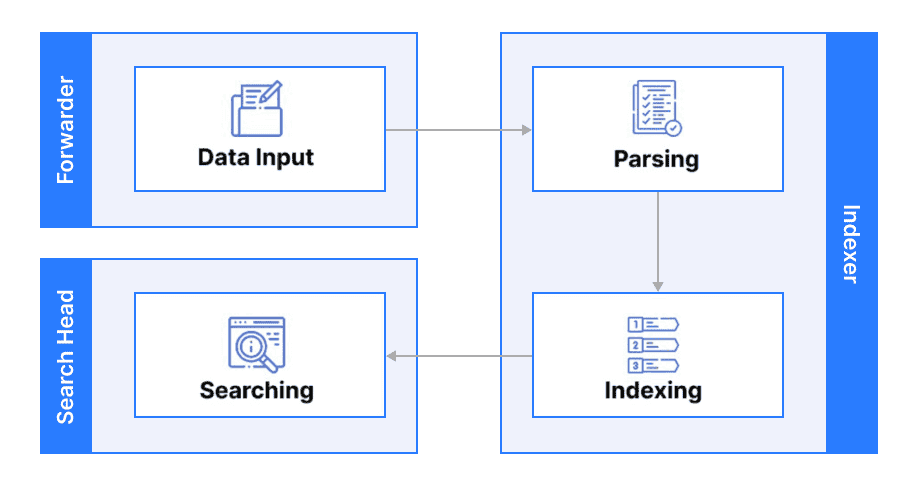
Data Ingestion: Splunk excels at ingesting and indexing diverse data sources using its universal forwarder. It parses raw data into a structured format for easy analysis.
Indexer Cluster: Splunk's Indexer Cluster provides high availability and fault tolerance. It distributes data across multiple indexers, optimizing search performance and system reliability.
Search Head Cluster: The Search Head Cluster enables parallel searches, dramatically reducing query response times and improving data retrieval efficiency.
Forwarder Management: Splunk simplifies forwarder management through careful configuration and monitoring, ensuring smooth data delivery to indexers.
Publishing Your App on Splunkbase
App Development & Validation
Get guidance on Splunk’s app development standards. We are here to make sure your app meets coding, packaging, and security best practices.
Splunk AppInspect Compliance
Run your app through Splunk AppInspect to validate functionality, security, and compatibility before submission.
Documentation & Metadata Configuration
Documentation and correct configurations are crucial. Our team will help you out with user guides, release notes, and app metadata for seamless user adoption.
Splunkbase Submission & Approval
We manage the submission process, address any review feedback, and ensure your app gets listed successfully on Splunkbase.
Splunk Use Cases
Advanced Security Monitoring & Threat Detection
Splunk, a powerful SIEM platform, aggregates logs from multiple sources, detecting anomalies, and enabling real-time threat detection. Security teams leverage its analytics and machine learning capabilities to proactively identify and mitigate cyber threats.
IoT & OT Security Visibility
Splunk integrates with IoT and OT security platforms to collect and analyze asset event data. By leveraging REST API connections, one can enhance visibility into industrial environments, detect anomalies, and strengthen their security posture.
Automated Vulnerability Management
With the NVD-CVE Fetcher App, Splunk continuously updates vulnerability databases, helping you track and respond to the latest security threats.
Threat Intelligence & Incident Response
Integrating Splunk with external threat intelligence platforms enhances its ability to correlate external data with internal security logs, and with this, security teams can automate alerting and incident response workflows.
IT Service Automation & SOC Efficiency
Splunk streamlines IT and security operations by integrating with platforms like ServiceNow. Automated incident creation based on Splunk alerts can reduce manual intervention and speed up security response times.
Cloud Security Monitoring & Compliance
Splunk helps organizations monitor cloud environments by collecting and analyzing security data from multi-cloud infrastructures. It detects misconfigurations, and ensures compliance with security frameworks.
Related Articles
How Splunk Enterprise Security Strengthens Your Operational Technology Security
Explore how Splunk ES can impact your organization's security posture.
Continue Reading →
Keep Your Splunk App Strong: Top 5 Post-Release Tips
Expert strategies to maintain, test, and future-proof your Splunkbase app.
Continue Reading →
Prepare Your Splunk Apps for 2025: Critical Updates You Should Know About
Everything you need to know about the latest Splunk critical updates.
Continue Reading →Similar Connectors



Splunk NVD-CVE Fetcher App
Installation Guide