Secure Identities, Cloud, and Endpoints with Microsoft Solutions
Overview
Microsoft's security portfolio delivers a comprehensive approach, encompassing identity and access management (Microsoft Entra), threat protection (Microsoft Defender), and security information and event management (Microsoft Sentinel). They emphasize cloud security with Defender for Cloud and data protection through Microsoft Purview.
Key Products
Microsoft Sentinel
A cloud-native security information and event management (SIEM) platform with AI-powered analytics. It collects and analyzes security data across an organization to detect and respond to threats.
Microsoft Defender
A suite of security solutions that provide extended detection and response (XDR) across endpoints, identities, email, and applications. It helps detect, investigate, and mitigate threats in real time.
Microsoft Entra ID
A collection of identity and access management tools (IAM) that verify user identities, enforce access controls, and secure authentication across cloud and on-premises environments.
Microsoft Purview
A data security and compliance solution that can classify, manage, and protect sensitive information while ensuring compliance with regulatory requirements.
Microsoft Priva
A privacy management tool that helps you track personal data usage, manage compliance with privacy laws, and reduce risks associated with sensitive data handling.
Microsoft Intune
A cloud-based endpoint management solution that allows you to configure security policies, manage devices, and protect corporate data on both company-owned and personal devices.
Microsoft Integrations
Microsoft Defender XDR + IoT: The integration of Microsoft Defender XDR with IoT security solutions strengthens an organization's overall security posture by extending threat detection and response capabilities to IoT devices.
Microsoft Sentinel + TIP: This integration connects a Threat Intelligence Platform (TIP) with Microsoft Sentinel, creating a unified threat monitoring and analysis workflow. By converting TIP logs into Sentinel-compatible formats, the integration enables security teams to leverage Sentinel's powerful analysis capabilities for TIP-generated alerts.
Microsoft Defender XDR + XSOAR + IoT: This integration aims to enhance device context, improve risk assessment, and streamline security operations. This also helps in enriching device context and risk assessment by fetching and mapping device data from Defender XDR to XSOAR, then populating the IoT platform with critical attributes and risk scores.
Microsoft Entra ID + XSOAR + IoT: Entra ID (formerly Azure AD) manages IT infrastructure, including user access and device authentication. The XSOAR platform acts as the bridge between Entra ID and the IoT platform. It facilitates the seamless flow of device data from Entra ID to the IoT devices.
Microsoft Defender XDR + XSOAR + IoT: In this integration, the data is fetched from MS Defender while the XSOAR platform maps the data based on the requirements of the IoT platform.
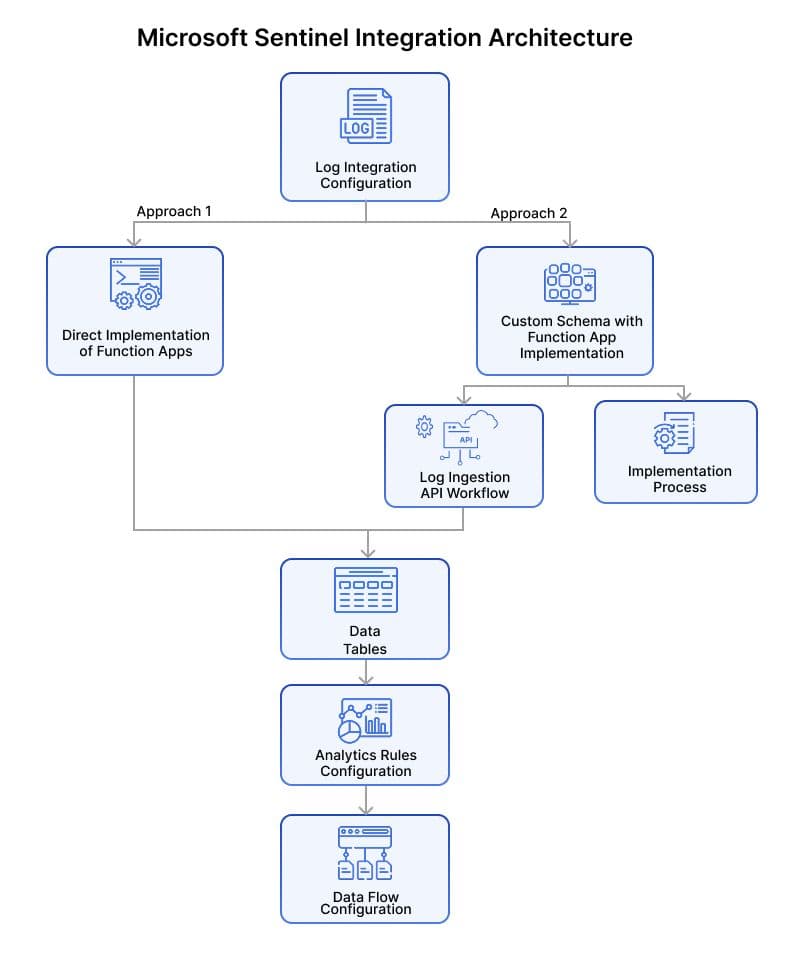
Microsoft Sentinel Integration Architecture
- Create Function App in Azure portal
- Configure authentication
- Transform unstructured logs
- Validate data transmission
- Analyze existing log structure
- Design compatible schema
- Implement mapping logic
- Validate log transformations
Approach 1: Direct Function Apps
Utilize Azure Function Apps for serverless log processing and follow the steps below:
Approach 2: Custom Schema with Function App
Create a tailored data structure mapping DRP logs to Sentinel requirements and go through the steps listed below:
Key Microsoft Security Integration Capabilities:
Proactive Threat Detection & Investigation
We leverage Microsoft Defender XDR’s AI-driven analytics to detect, correlate, and analyze threats in real time, ensuring faster and more effective investigations.
Streamlined Workflows & Operational Efficiency
Through integration, consolidate security data into a single centralized view and eliminate the need to switch between multiple consoles. We will help you maximize your productivity.
Unified Threat Hunting
Empower your security teams with advanced threat-hunting capabilities by combining Microsoft Defender XDR’s insights with SIEM data to proactively detect and neutralize hidden threats.
Improved Security Visibility
Integrate endpoints, networks, and cloud sources to provide comprehensive security visibility, we are here to help you identify and close security gaps before they become critical risks.
Integration Use Cases
Leverage Microsoft Security Architecture
Ensures integration is seamless, secure, and aligned with best practices to enhance protection, optimize performance, and strengthen your overall security posture.
Use Microsoft Graph Security API
Microsoft Graph Security API is a centralized interface used to access alerts, actions, and threat intelligence across the Microsoft ecosystem.
Analyse and Automate Microsoft Sentinel
Use KQL (Kusto Query Language) for creating custom queries and analytics, and Automate response actions using playbooks with Azure Logic Apps.
Threat Detection with Microsoft Defender for Endpoint
Deploy agents or integrate with existing endpoint management solutions to improve security visibility and ensure proactive endpoint detection and protection.
Connect using Entra ID
Use APIs to enable SSO, MFA, and conditional access policies, and synchronize users and groups using Entra ID for secure and efficient identity management.
Microsoft Defender for Cloud
Use Azure Policy to enforce security standards, maintain compliance, and strengthen cloud security by applying best practices.
Similar Connectors