Strengthen Security with Google Cloud Solutions
Overview
Google's cybersecurity strategy focuses on secure cloud infrastructure (GCP), advanced threat detection (SecOps), and secure collaboration (Workspace). Google leverages its AI and infrastructure to provide layered security, aiming for proactive protection across its cloud and enterprise services.
Key Products
Google SecOps
Google Security Operations (SecOps), formerly known as Chronicle, is a cloud service that enables enterprises to securely retain, analyze, and search vast amounts of security and network telemetry, helping them detect threats and respond efficiently.
Google Cloud Platform
Google Cloud Platform (GCP) offers a mix of cloud solutions, combining scalable infrastructure, AI-driven analytics, and top-tier security. With tools like Google Cloud IAM for access control and the Security Command Center for threat detection, GCP helps organizations stay secure and compliant.
Google Workspace
Google Workspace is a cloud-based suite of productivity and collaboration tools designed to help individuals, teams, and organizations work efficiently. With integrated apps accessible from anywhere, it supports remote and hybrid work environments for seamless teamwork.
Google Security Operations - Integrations
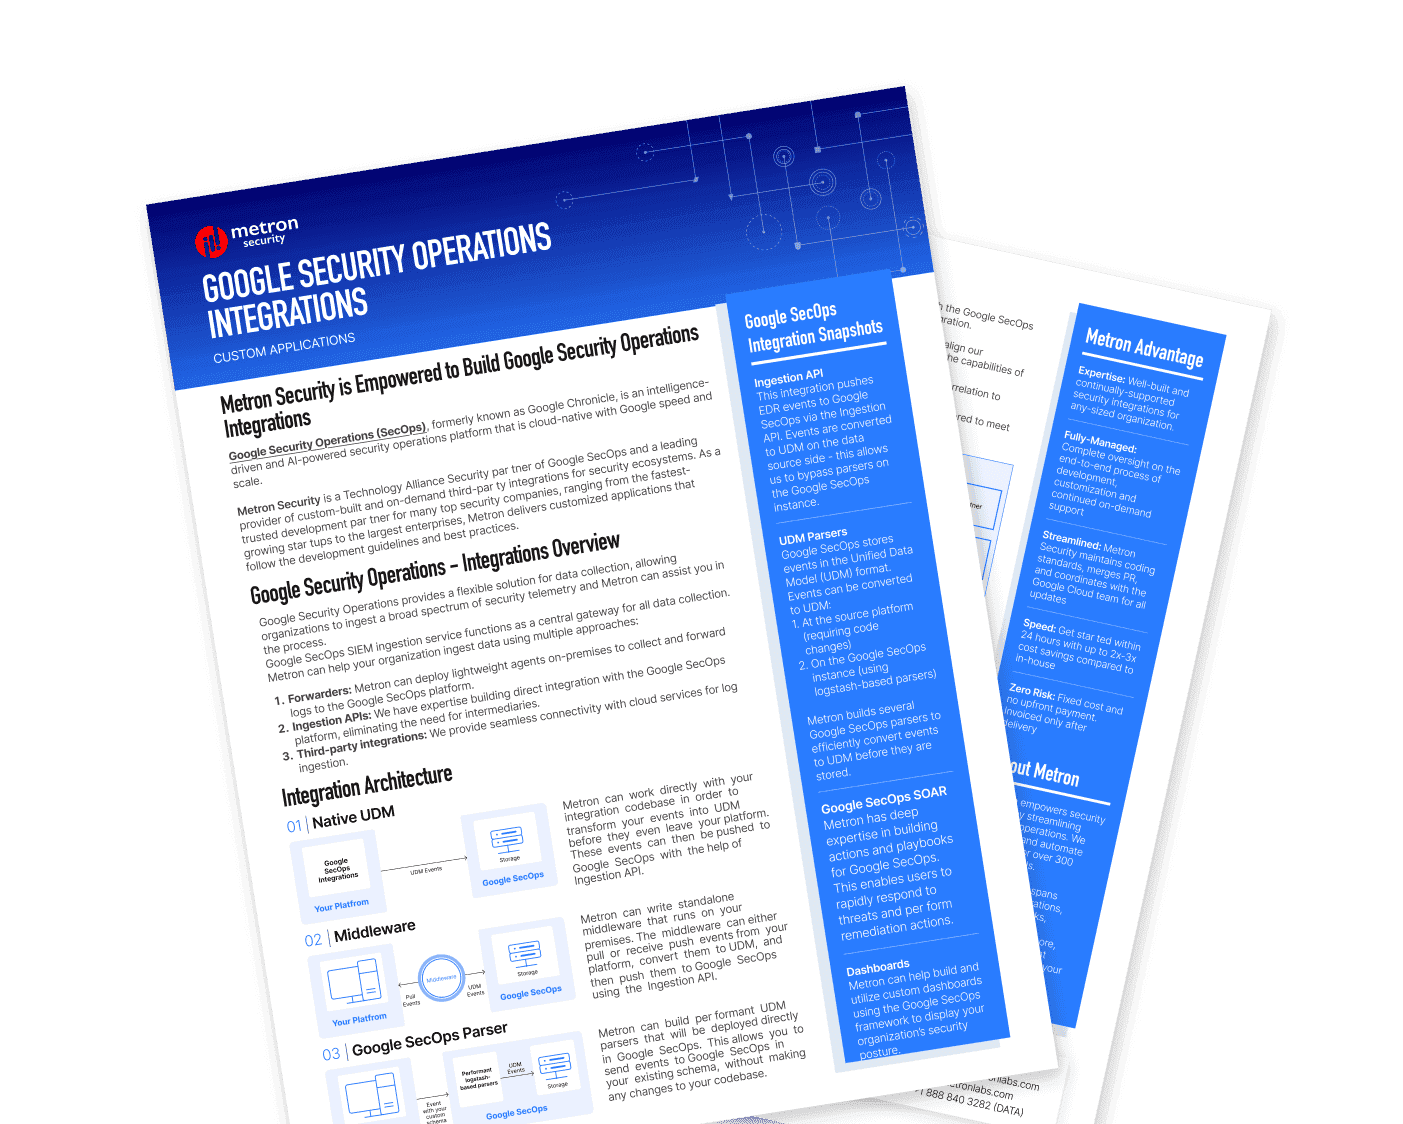
Google Security Operations provides a flexible solution for data collection, allowing organizations to ingest a broad spectrum of security telemetry—and Metron can assist you in the process. Google SecOps SIEM ingestion service functions as a central gateway for all data collection. Metron can help your organization ingest data using multiple approaches:
Forwarders: Metron can deploy lightweight agents on-premises to collect and forward logs to the Google SecOps platform.
Ingestion APIs: We have expertise building direct integration with the Google SecOps platform, eliminating the need for intermediaries.
Third-party integrations: We provide seamless connectivity with cloud services for log ingestion.
Streamlined Process
The proposed methodology for developing a parser in collaboration with the Google SecOps team offers a comprehensive approach to building a highly efficient integration. Key aspects include:
Optimized Integration: Collaborating with the Google SecOps team to align our development process, ensuring the parser is designed to fully leverage the capabilities of both platforms.
DF Enhanced Performance: Fine-tuning data ingestion, normalization, and correlation to boost security telemetry analysis and system efficiency.
SF Scalability and Customization: Delivering a scalable, adaptable solution tailored to meet the evolving needs of shared customers.

Google SecOps Integration Snapshots
Ingestion API
This integration pushes EDR events to Google SecOps via the Ingestion API. Events are converted to UDM on the data source side - this allows us to bypass parsers on the Google SecOps instance.
UDM Parsers
Google SecOps stores events in the Unified Data Model (UDM) format. Events can be converted to UDM:
- At the source platform (requiring code changes).
- On the Google SecOps zinstance (using logstash-based parsers).
Metron builds several Google SecOps parsers to efficiently converedt events to UDM before they are stored.
Google SecOps SOAR
Metron has deep expertise in building actions and playbooks for Google SecOps. This enables users to rapidly respond to threats and per form remediation actions.
Dashboards
Metron can help build and utilize custom dashboards using the Google SecOps framework to display your organization’s security posture.
Integration Architecture
Native UDM
Metron can work directly with your integration codebase in order to transform your events into UDM before they even leave your platform. These events can then be pushed to Google SecOps with the help of the Ingestion API.
Middleware
Metron can write standalone middleware that runs on-premises. The middleware can either pull or receive push events from your platform, convert them to UDM, and then push them to Google SecOps using the Ingestion API.
Google SecOps Parser
Metron can build performant UDM parsers that will be deployed directly in Google SecOps. This allows you to send events to Google SecOps in your existing schema, without making any changes to your codebase.
Similar Connectors



Google Security
Operations Integrations