Fortify Your Workload with CrowdStrike's AI-Native Security
Overview
CrowdStrike delivers cloud-based endpoint security solutions that unify threat prevention, detection, and response into a single lightweight agent. The CrowdStrike Falcon platform provides comprehensive protection and real-time visibility across enterprise environments. CrowdStrike Falcon Prevent enables advanced threat prevention with machine learning and behavioral analytics for reliable protection. The CrowdStrike Falcon XDR platform delivers extended detection and response capabilities with robust threat hunting, incident investigation, and automated remediation services to ensure comprehensive security across the entire IT ecosystem.
Key Products
Falcon Platform
Forms the backbone of endpoint security, providing a cloud-native platform for centralized detection, prevention, and response across all endpoints. Falcon delivers comprehensive visibility, AI-powered threat intelligence, and automated workflows that simplify security operations while offering protection against sophisticated threats across distributed environments.
Falcon Endpoint
Delivers complete endpoint protection through a unified agent architecture that combines next-generation antivirus, endpoint detection and response, and managed threat hunting capabilities. Falcon Endpoint provides real-time visibility into endpoint activities, automated detection of suspicious behaviors, and rapid response options, including remote containment and remediation.
Falcon Prevent
Orchestrates the entire threat prevention lifecycle, from malware blocking and exploit prevention to advanced behavioral protection and machine learning analysis. Falcon Prevent automates security functions, facilitates proactive defense, and provides a centralized platform for controlling security policies, minimizing breach potential, and ensuring reliable endpoint protection.
Falcon XDR
Streamlines the process of threat detection, investigation, and response across heterogeneous technology environments. Falcon XDR delivers granular visibility, automated threat hunting, and comprehensive analysis of security telemetry, minimizing dwell time and ensuring only legitimate activities continue while efficiently isolating and remediating threats.
Falcon Intel
Provides actionable threat intelligence derived from CrowdStrike's global sensor network and expert human analysis. Falcon Intel delivers contextualized adversary profiles, indicators of compromise (IOCs), and strategic intelligence reports that help organizations understand the threat landscape.
Zero Trust
Implements identity-based security controls that continuously verify and validate users and devices before granting access to resources. CrowdStrike Zero Trust integrates endpoint health and security posture into authentication decisions, enabling conditional access based on real-time risk assessment.
Charlotte AI
Enhances the Falcon platform with advanced artificial intelligence capabilities for automated threat detection, investigation, and response. Charlotte AI provides security analysts with natural language query capabilities to rapidly search and analyze security telemetry across the enterprise.
Falcon LogScale
Delivers enterprise-scale log management and real-time observability through a high-performance analytics platform designed for modern security operations. Falcon LogScale ingests massive volumes of security and operational data with sub-second latency, enabling immediate visibility across complex environments.
Falcon Fusion SOAR
Streamlines security operations through automated workflow orchestration and response capabilities built natively into the Falcon platform. Falcon Fusion SOAR enables security teams to create customized playbooks that automate repetitive tasks, standardize response procedures, and accelerate incident handling across the entire security stack.
CrowdStrike Integrations
CrowdStrike Falcon Endpoint + SIEM: The integration between CrowdStrike Falcon Endpoint and SIEM enhances security operations by combining endpoint protection with security analytics. This integration allows for a deeper analysis of endpoint activity by correlating it with other security data sources within the SIEM platform.
Cloud-Native Integration Architecture of Falcon
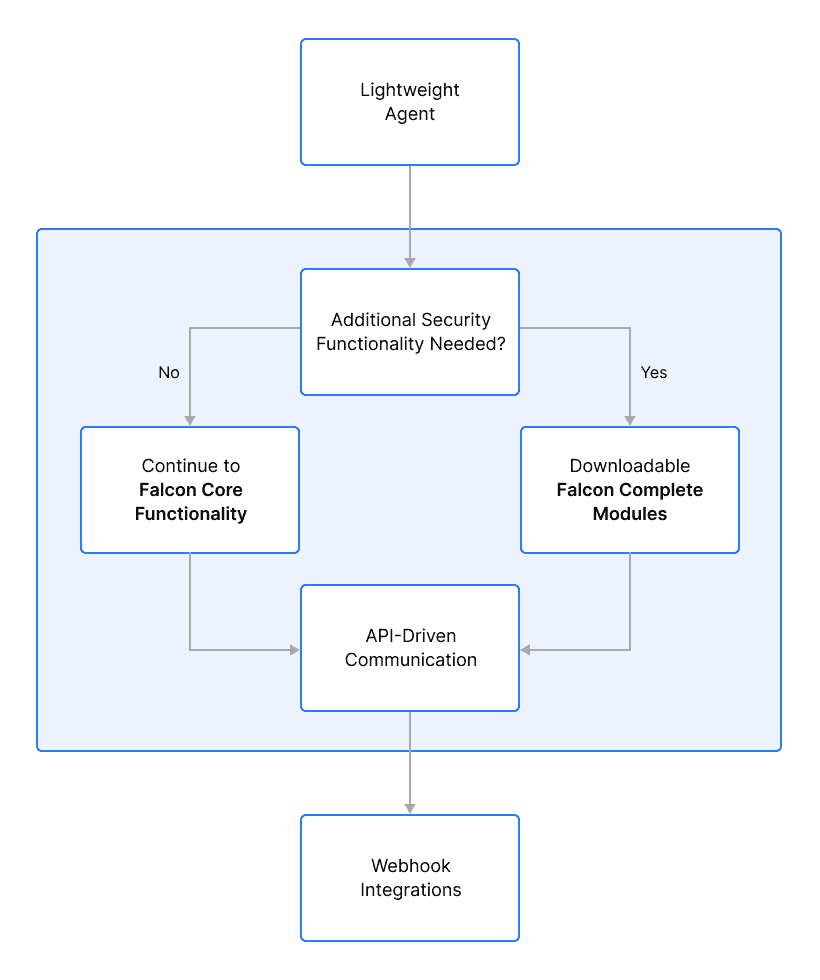
CrowdStrike Falcon's integration capabilities provide a comprehensive foundation for building highly efficient security workflows with minimal operational overhead. Key architectural components include:
- Lightweight Agent - An agent that handles all Falcon data collection and enforcement across endpoints with minimal resource impact. This unified architecture eliminates the need for multiple security agents, simplifying deployment and management.
- Falcon Complete Modules - Extend core agent capabilities through downloadable modules that maintain the lightweight design while adding specialized security functions. Integration occurs at the agent level, allowing precise control over data collection based on enabled modules.
- API-Driven Communication - Well-documented APIs enable external platforms to interact with Falcon's data and functions. Security teams can programmatically access threat intelligence and endpoint status and execute security controls, facilitating deep integration and workflow automation.
- Webhook Integrations - Real-time notification channels that trigger immediate automated responses to specific security events. When critical threats like ransomware are detected, webhooks instantly alert connected systems to execute pre-defined containment and remediation workflows.
Falcon Architectural Benefits
Enhanced Threat Detection
Integrate threat intelligence feeds (CTI) to enrich Falcon's native threat detection capabilities. CTI feeds can be incorporated through Falcon Open XDR or pre-built connectors within the CrowdStrike Store. This enables Falcon to identify even the most sophisticated threats by incorporating the latest knowledge.
Unified Security Operations
Integrate Falcon with your SIEM or SOAR platform. This allows security analysts to view real-time data from Falcon alongside events from other security tools within a single dashboard. This centralized view, facilitated by the underlying architecture, allows for faster and more efficient threat investigation and response.
Automated Workflows for Faster Response
Utilize Falcon's webhooks and API capabilities to trigger automated workflows within your existing security stack. This can automate crucial actions like isolating compromised endpoints, quarantining threats, or initiating remediation procedures. This minimizes human intervention and ensures a swift response to security incidents, all thanks to the real-time communication channels enabled by the architecture.
Use Cases
Comprehensive Endpoint Protection with Falcon Platform
Leverage Falcon's lightweight agent to implement next-generation antivirus, endpoint detection and response, and threat hunting across the enterprise.
Cloud Workload Protection
CrowdStrike Falcon can protect cloud workloads across multiple cloud providers, providing a unified view for efficient security management and compliance.
Automated Response Actions
By integrating with IT service management platforms, CrowdStrike products can automate the process of isolating compromised endpoints, blocking malicious processes, and remediating threats, reducing mean time to resolution.
AI-Powered Threat Intelligence
Falcon's global intelligence capabilities help prioritize security alerts based on factors like severity, adversary tactics, and organizational impact, ensuring that security teams focus on the most critical threats first.
Rapid Incident Response
When a security incident is detected, CrowdStrike Falcon can automatically trigger containment actions and provide detailed forensic data for comprehensive investigation and root cause analysis.
Efficient Log Aggregation and Correlation
Next-gen SIEMs like LogScale intelligently aggregate and correlate log data from diverse sources, providing your security team with a unified view.
Similar Connectors