Unify Enterprise Security with Symantec by Broadcom
Key Products
Symantec Endpoint Security Complete
Unified endpoint protection, detection, and response (EDR) powered by a single agent to secure traditional, mobile, and cloud workloads.
Symantec Data Loss Prevention
Enterprise-wide data protection that discovers, monitors, and guards sensitive data across endpoint, cloud, network, and storage channels.
Symantec Secure Web Gateway
Advanced web security and threat isolation platform offering deep packet inspection and safe encrypted traffic management.
Symantec Integration Architecture
Symantec connects with external security and IT platforms through secure REST APIs and ICDx integrations. Endpoint events and threat alerts are collected and shared across connected systems, helping teams synchronize security data, automate workflows, and accelerate threat detection and response.
Architecture
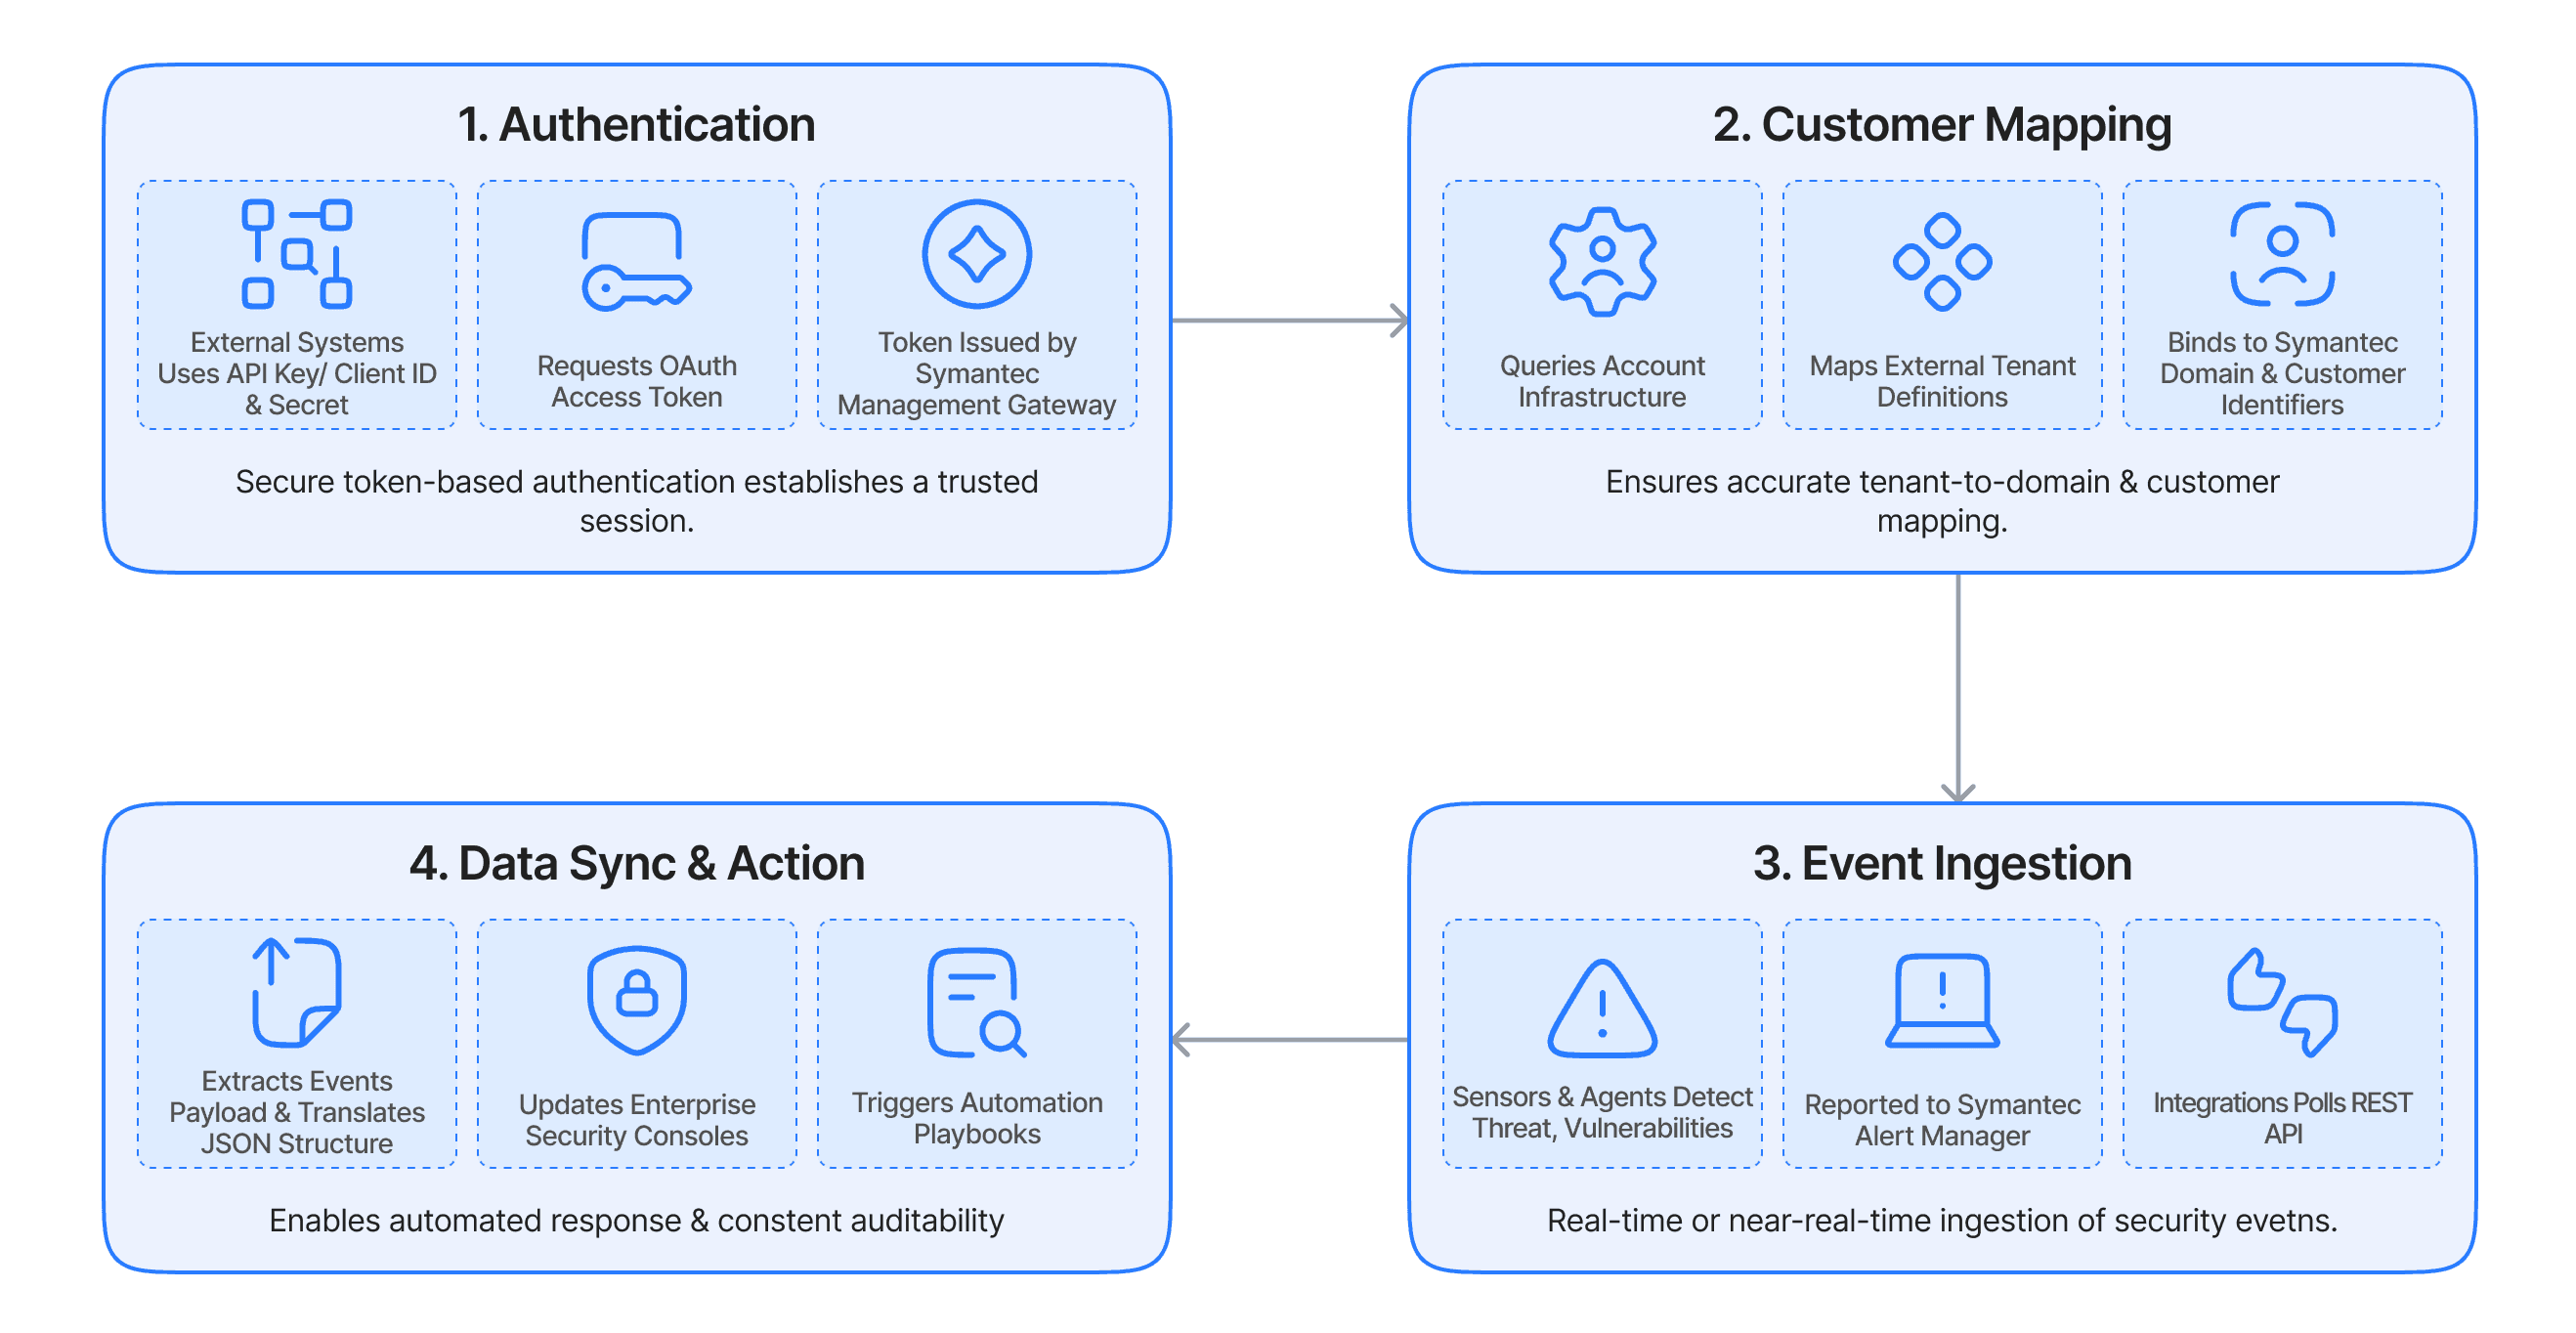
1. Authentication: The external system initiates a session using an enterprise API key or Client ID and Secret to securely request an API access token from the Symantec management gateway.
2. Data Mapping: The integration queries the account infrastructure to bind external tenant definitions safely to corresponding Symantec domain and customer identifiers.
3. Event Ingestion: Symantec sensors and endpoint agents detect vulnerabilities, anomalous network behavior, or security threats and report them to the Symantec Alert Manager. The integration layer polls the REST API or consumes the ICDx stream to forward alerts to the connected SIEM/SOAR platform.
4. Workflow Actions: After ingestion and mapping, the data can trigger automated responses, update downstream workflows, or be recorded for audit and reporting.
Symantec Integration Benefits
REST API & JSON Data Ingestion
Standard HTTP-based endpoints returning formatted JSON data for programmatic querying of threat telemetry, asset states, and administrative tasks.
ICDx (Integrated Cyber Defense Exchange)
A centralized event bus and normalization engine designed to collect, translate, and stream Symantec event logs directly into third-party SIEMs and data lakes.
WebSocket Streams
Real-time bi-directional streaming interfaces designed to push malware verdicts, live analysis, and high-frequency alerts directly to external systems.
SOAR Action & Playbook Hooks
Execution connectors allowing security orchestrators to remotely trigger containment, file blocking, and device isolation on Symantec management consoles.
Integration Use Cases
Automated Operational Syncing
This Integration accelerates the service delivery by linking device enrollment and security policy updates directly to your IT management pipelines. When you add a new device or tenant, the integration automatically provides matching security profiles inside Symantec.
Centralized Security Contextualization
This Integration optimises threat triage by routing live alerts and threat intelligence into a single operational center. Analysts can track malware detections, network events, and EDR telemetry alongside machine data without switching tabs.
Fail-Safe Remediation Orchestration
This Integration reinforces system stability with automated, cross-platform playbooks. For example, an external monitoring alert or EDR incident can trigger an instant host isolation or policy update right before remediation, ensuring rapid threat containment.
Similar Connectors