Unify Endpoint Security and Management with Tanium
Key Products
Tanium Autonomous IT Platform
Unified endpoint management and security platform combining real-time asset discovery, threat detection, configuration management, and automated remediation on a single agent.
Tanium Endpoint Management
Delivers continuous asset discovery, autonomous patch management, software deployment, and configuration control across physical, virtual, and mobile endpoints.

Tanium Threat Response & Exposure Management
Detects, investigates, and responds to threats in real time while continuously scoring vulnerability risks, prioritizing exposures, and deploying automated fixes.
Tanium Integration Architecture
Tanium connects with external security and IT platforms through secure REST and GraphQL APIs or native integrations. Endpoint data, vulnerability insights, and security alerts are collected and shared with connected systems to synchronize asset inventories, automate workflows, and accelerate incident response.
Architecture
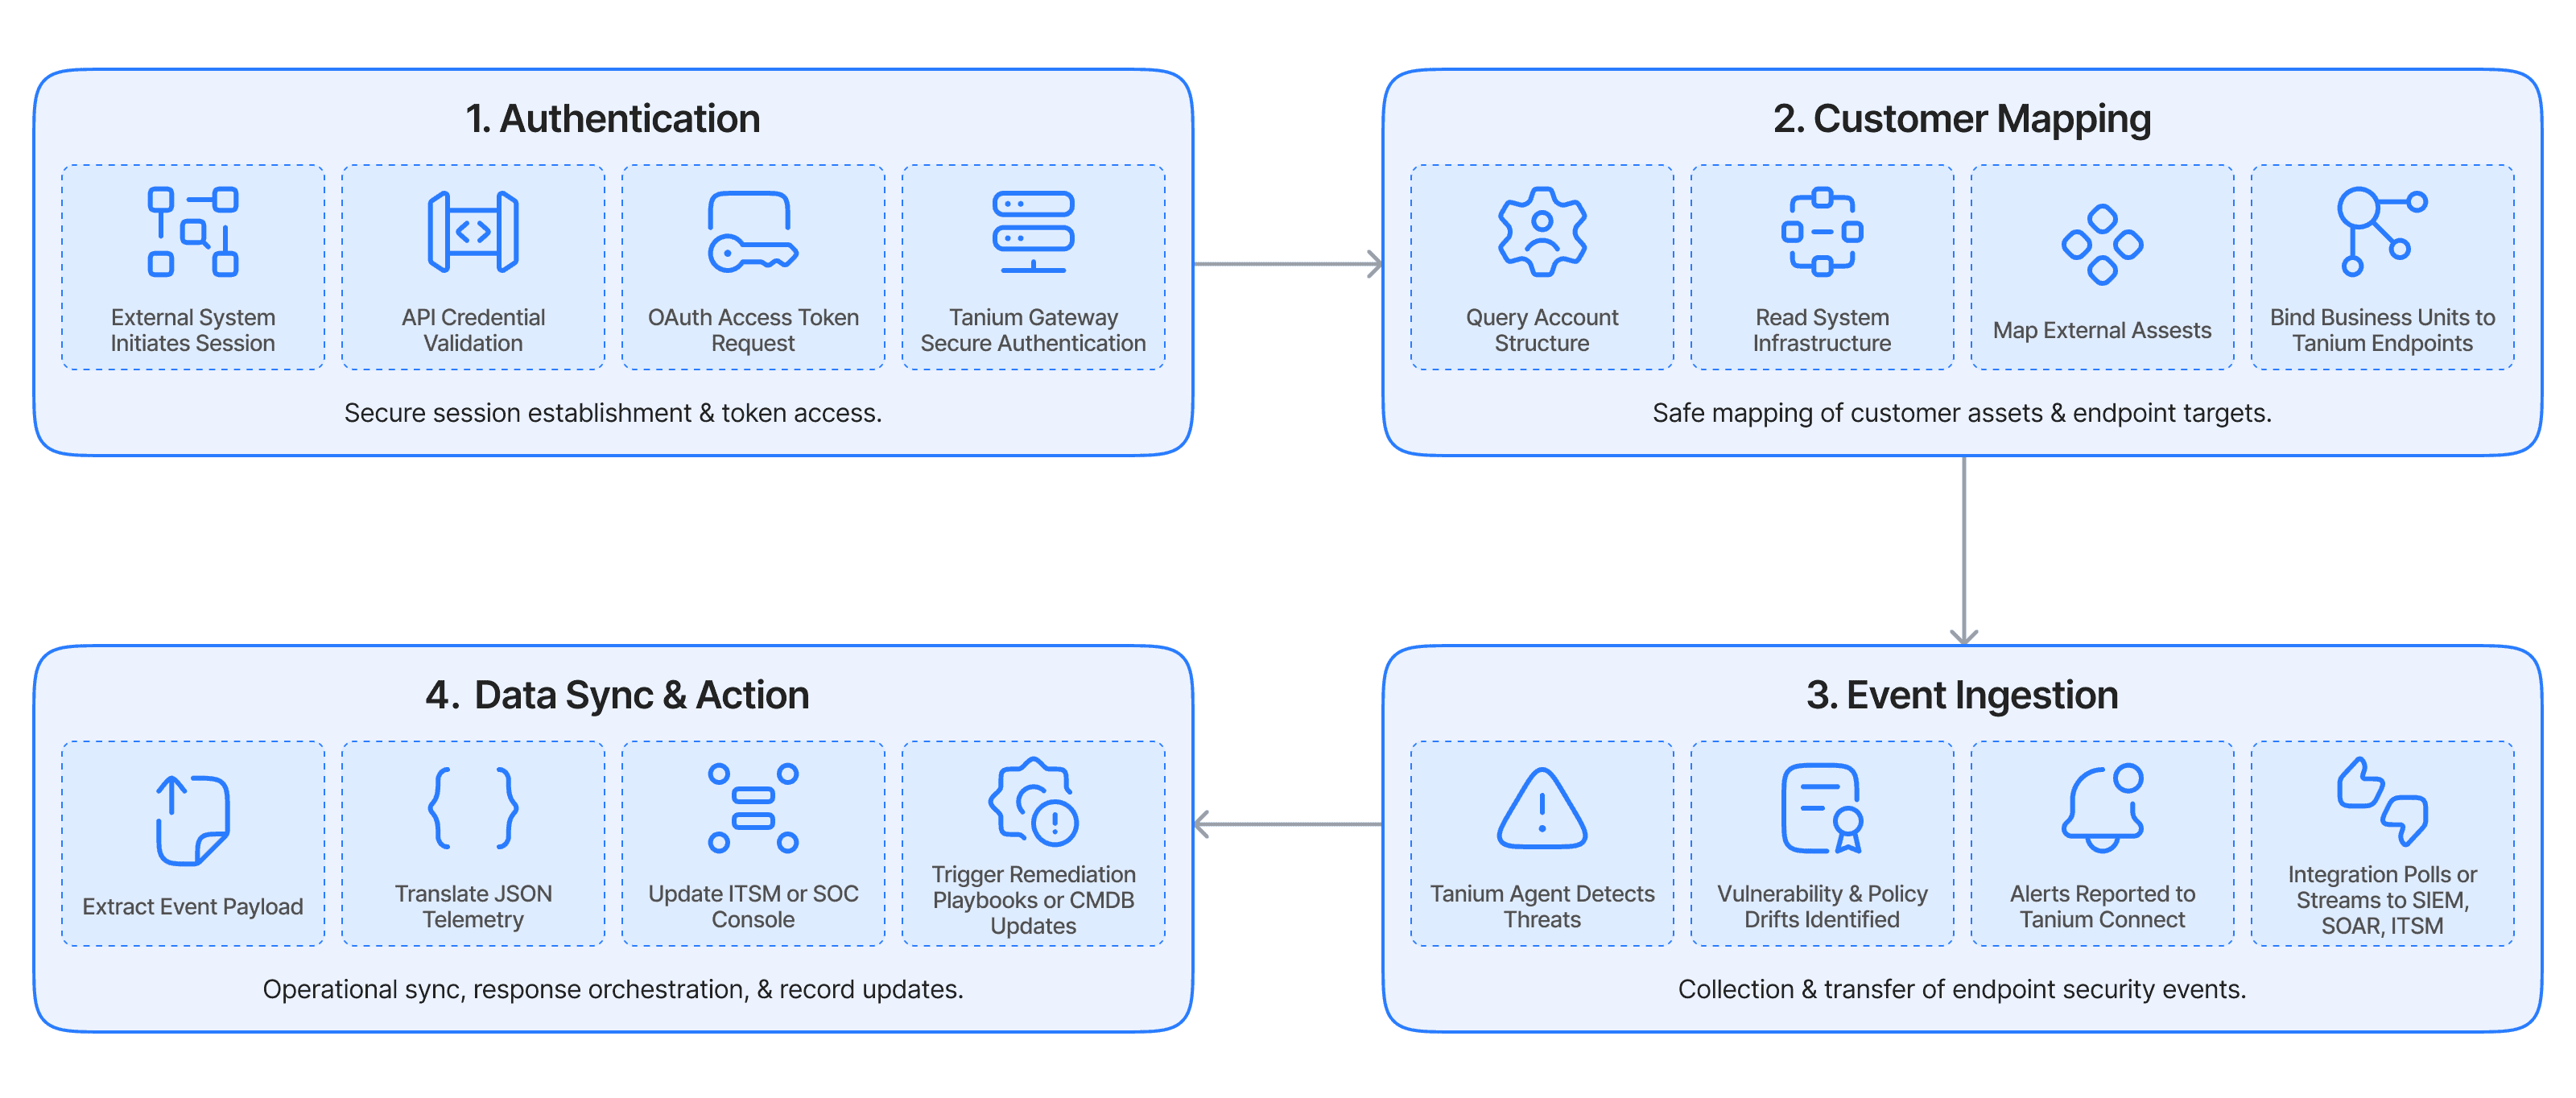
1. Authentication: The external system authenticates with the Tanium platform using a configured API token or requests a temporary session token using valid system credentials.
2. Customer Mapping: The integration queries the account and system infrastructure to bind external asset definitions and business units safely to corresponding Tanium endpoint targets.
3. Event Ingestion: The Tanium endpoint agent detects security threats, unpatched vulnerabilities, or policy drifts and reports them to Tanium Connect. The integration layer polls or streams these alerts directly to the connected SIEM, SOAR, or ITSM platform.
4. Data Sync & Action: The integration layer extracts the event payload, translates the JSON telemetry, and updates the external ITSM or SOC console to run automated remediation playbooks or update CMDB records.
Tanium Integration Benefits
Inbound Connectors & Dashboard Apps
Embeds real-time Tanium endpoint insights natively inside external SOC and IT consoles, giving security analysts multi-tenant monitoring, interactive widgets, and unified reporting in one tab.
Ticket & Incident Bridge Alerting
Connects Tanium system alerts, vulnerability risks, and threat events directly to external ITSM or SOAR platforms (such as ServiceNow and Splunk) to auto-generate tracking tickets and playbooks.
Tanium Gateway GraphQL API
Leverages Tanium’s primary GraphQL interface to perform flexible endpoint queries, retrieve live asset telemetry, and trigger mutations programmatically.
Targeted Action Scripting Integration
Deploys custom execution packages, registry fixes, and isolation commands through the Tanium Client agent, augmenting out-of-the-box response frameworks on targeted endpoints.
Integration Use Cases
Automated Operational Syncing
We accelerate service delivery by linking endpoint discovery directly to your ITSM or CMDB pipelines. When you deploy or update hardware assets, the integration automatically provisions matching inventory definitions and syncs real-time configuration state inside Tanium.
Centralized Security Contextualization
We optimize threat triage by routing live endpoint telemetry into a single operational center. Analysts can track patch compliance, active processes, and vulnerability metrics alongside network telemetry without switching tabs.
Fail-Safe Remediation Orchestration
We reinforce system stability with automated, cross-platform playbooks. For example, an external security alert can trigger an instant Tanium endpoint isolation or targeted patch deployment, ensuring a rapid containment response in seconds.
Similar Connectors