Secure, Automate, and Govern Every Identity Across Your Entire Enterprise Hybrid Footprint
Overview
SailPoint helps organizations manage and secure human and non-human identities across cloud, SaaS, and on-premises environments. By connecting SailPoint with ITSM, SIEM, HRIS, and PAM platforms, we help automate identity lifecycles, strengthen governance, and enforce access policies across your enterprise.
Key Products
SailPoint Identity Security Cloud (Human Fabric)
AI-driven SaaS identity governance and administration platform designed to automate access certification, lifecycle management, risk detection, and access recommendations across modern cloud environments.
SailPoint IdentityIQ
An enterprise-grade, on-premises identity security solution delivering granular access governance, compliance management, automated provisioning, and password management for complex hybrid deployments.
Non-Human Identity Management
Enterprise module designed to discover, track, and secure non-human accounts such as service accounts, bots, APIs, and machine identities, preventing privilege escalation and silent perimeter breaches.
Access Risk Management
Automated analysis solution that scans enterprise applications (like SAP and ERP environments) to continuously detect Separation of Duties (SoD) conflicts, financial risk, and toxic access combinations.
Data Access Security
Dedicated governance solution that extends identity controls to unstructured data repositories, discovering sensitive data in file shares, cloud storage, and collaboration tools to govern who has access to what.
Identity Outlier Detection
Machine-learning-driven analytics feature that flags anomalous access rights, unusual entitlement assignments, and high-risk user profiles by comparing user activity against peer groups.
SailPoint Integration Architecture
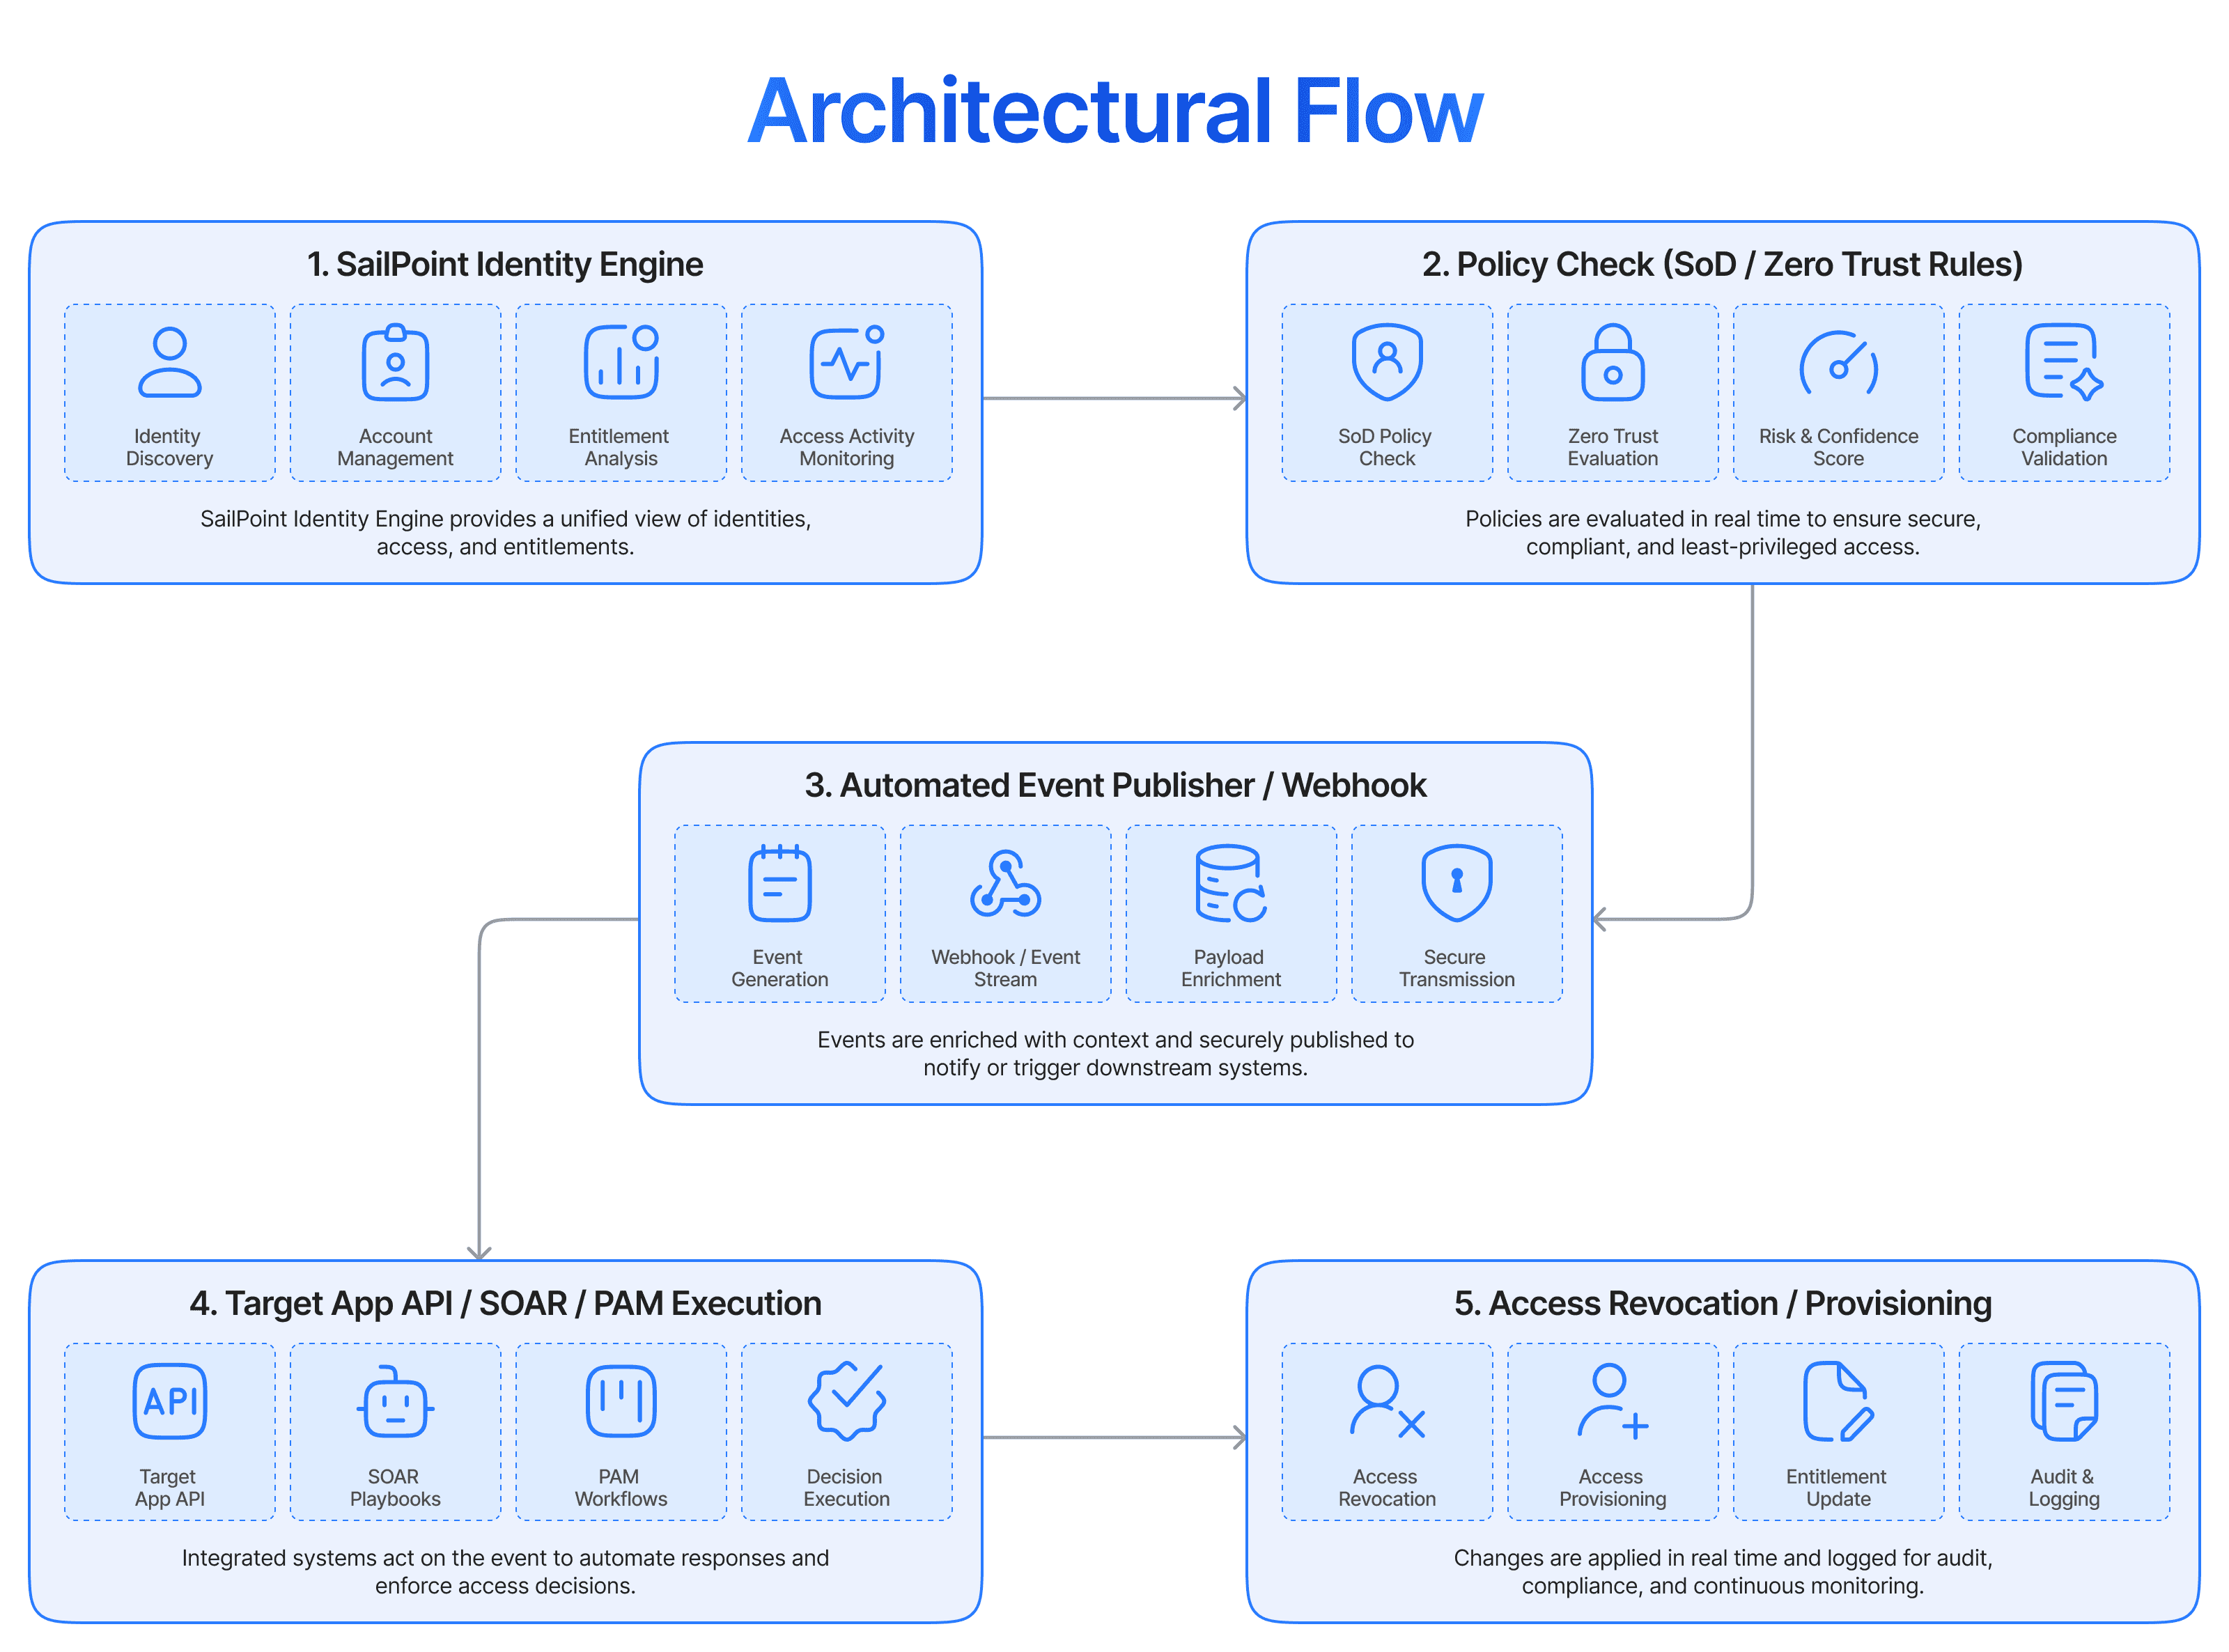
Data flows bidirectionally between the target third-party ecosystem and SailPoint. Source systems (HRIS, directories) push identity attributes and state changes to SailPoint. SailPoint correlates this telemetry against AI risk models, enforces governance policies, and pushes orchestrated provisioning commands or event alerts across target applications, PAM solutions, and security monitoring tools.
Streamlined Logic
1. Identity Telemetry Ingestion: SailPoint periodically pulls or receives real-time webhook signals from HR systems (e.g., Workday) and target applications detailing user attributes, roles, and current entitlement bindings.
2. Correlation & Policy Evaluation: The engine normalizes raw user attributes into a unified Identity Cube, evaluating access permissions against Segregation of Duties (SoD) rules, zero-trust policies, and AI risk baselines.
3. Event & Remediation Triggering: If an unauthorized change or high-risk outlier is detected (e.g., an employee changes roles or leaves), SailPoint generates an automated event trigger.
4. Orchestrated Action Execution: SailPoint calls target system APIs or triggers SOAR playbooks to revoke access, adjust PAM privileges, or log an incident in the SIEM.
5. Audit Logging & Verification: The final state is logged into the audit repository to provide continuous compliance visibility and complete audit trail reports.
SailPoint Integration Benefits
Out-of-the-Box (OOTB) Direct Connectors
Pre-built, deep-level connectors for enterprise software (such as Workday, ServiceNow, SAP, AWS, Microsoft Entra ID, and Salesforce) designed to read telemetry, manage accounts, and push entitlement changes directly.
SaaS Management Connectivity (SaaS Workflows)
Lightweight API-based connectors built to discover unsanctioned SaaS applications, map user activity, and govern shadow IT across third-party cloud apps.
Event Triggers & Webhooks
Real-time event publishing architecture that broadcasts identity events (e.g., employee termination, privilege change, risk score update) to third-party tools like SIEMs, SOARs, and messaging platforms via HTTP webhooks or Amazon EventBridge.
REST API & SCIM Standard Integration
Standardized open APIs allowing developers to write custom integrations, ingest identity data from proprietary databases, and execute custom provisioning actions using standard SCIM (System for Cross-domain Identity Management) endpoints.
ITSM Integration & Request Orchestration
Bidirectional connectors mapping identity workflows directly into enterprise ticketing engines (like ServiceNow or Jira Service Desk) for streamlined access requests and manual task fulfilment.
Integration Use Cases
Real-Time SOC & SOAR Event Ingestion
Connect identity governance directly with threat detection pipelines. When SailPoint identifies an anomalous access escalation or policy breach, it broadcasts real-time security events to your SIEM/SOAR platform, enabling security teams to automatically isolate compromised accounts and execute targeted access revocations.
Closed-Loop ITSM Fulfilment
Bridge governance policies with existing service desks. Access requests initiated in tools like ServiceNow are routed through SailPoint for automated risk checks and approval workflows, automatically executing the change in the endpoint application upon approval and updating the ticket status.
Unified Privileged Access Governance
Consolidate standard and privileged access management into a single pane of glass. By integrating SailPoint with PAM engines (like CyberArk or HashiCorp), we extend identity certification, access reviews, and audit controls to high-privilege administrative credentials and vaulted accounts.
Similar Connectors