Connect Identity Across Your Enterprise with Okta
Overview
Okta is a leading identity and access management platform that helps organizations securely connect people, applications, and devices. Built for modern enterprises, it provides single sign-on, multi-factor authentication, lifecycle management, and API security to simplify identity management and strengthen access control. Integrating with Okta extends secure authentication and identity workflows across your technology ecosystem, enabling seamless user experiences and stronger security.
Key Products
Okta Workforce Identity Cloud
A unified platform designed to manage and secure your employees, contractors, and partners. It streamlines daily productivity through single sign-on and context-aware multi-factor authentication.
Okta Customer Identity Cloud (Auth0)
A highly customizable identity platform for developer teams building customer-facing applications. It provides smooth login flows, social connection support, and robust privacy defense right out of the box.
Okta Workflows
A no-code automation engine that orchestrates complex identity and access tasks. It uses conditional logic and pre-built connectors to automate tasks like system alerts, app provisioning, and compliance reporting.
Okta Privileged Access (PAM)
An identity-first privileged access management solution that secures infrastructure, databases, and microservices by replacing static SSH/RDP keys with dynamic, just-in-time credentials.

Okta Identity Threat Detection & Response (ITDR)
A continuous monitoring solution that catches identity-focused vulnerabilities and active attacks. It ingests cross-platform risk signals to stop account takeovers and session hijacking instantly.
Okta Identity Governance (OIG)
An automated governance suite that unifies access request workflows and compliance-driven access reviews to enforce strict least-privilege policies across critical applications.
Okta Integration Architecture
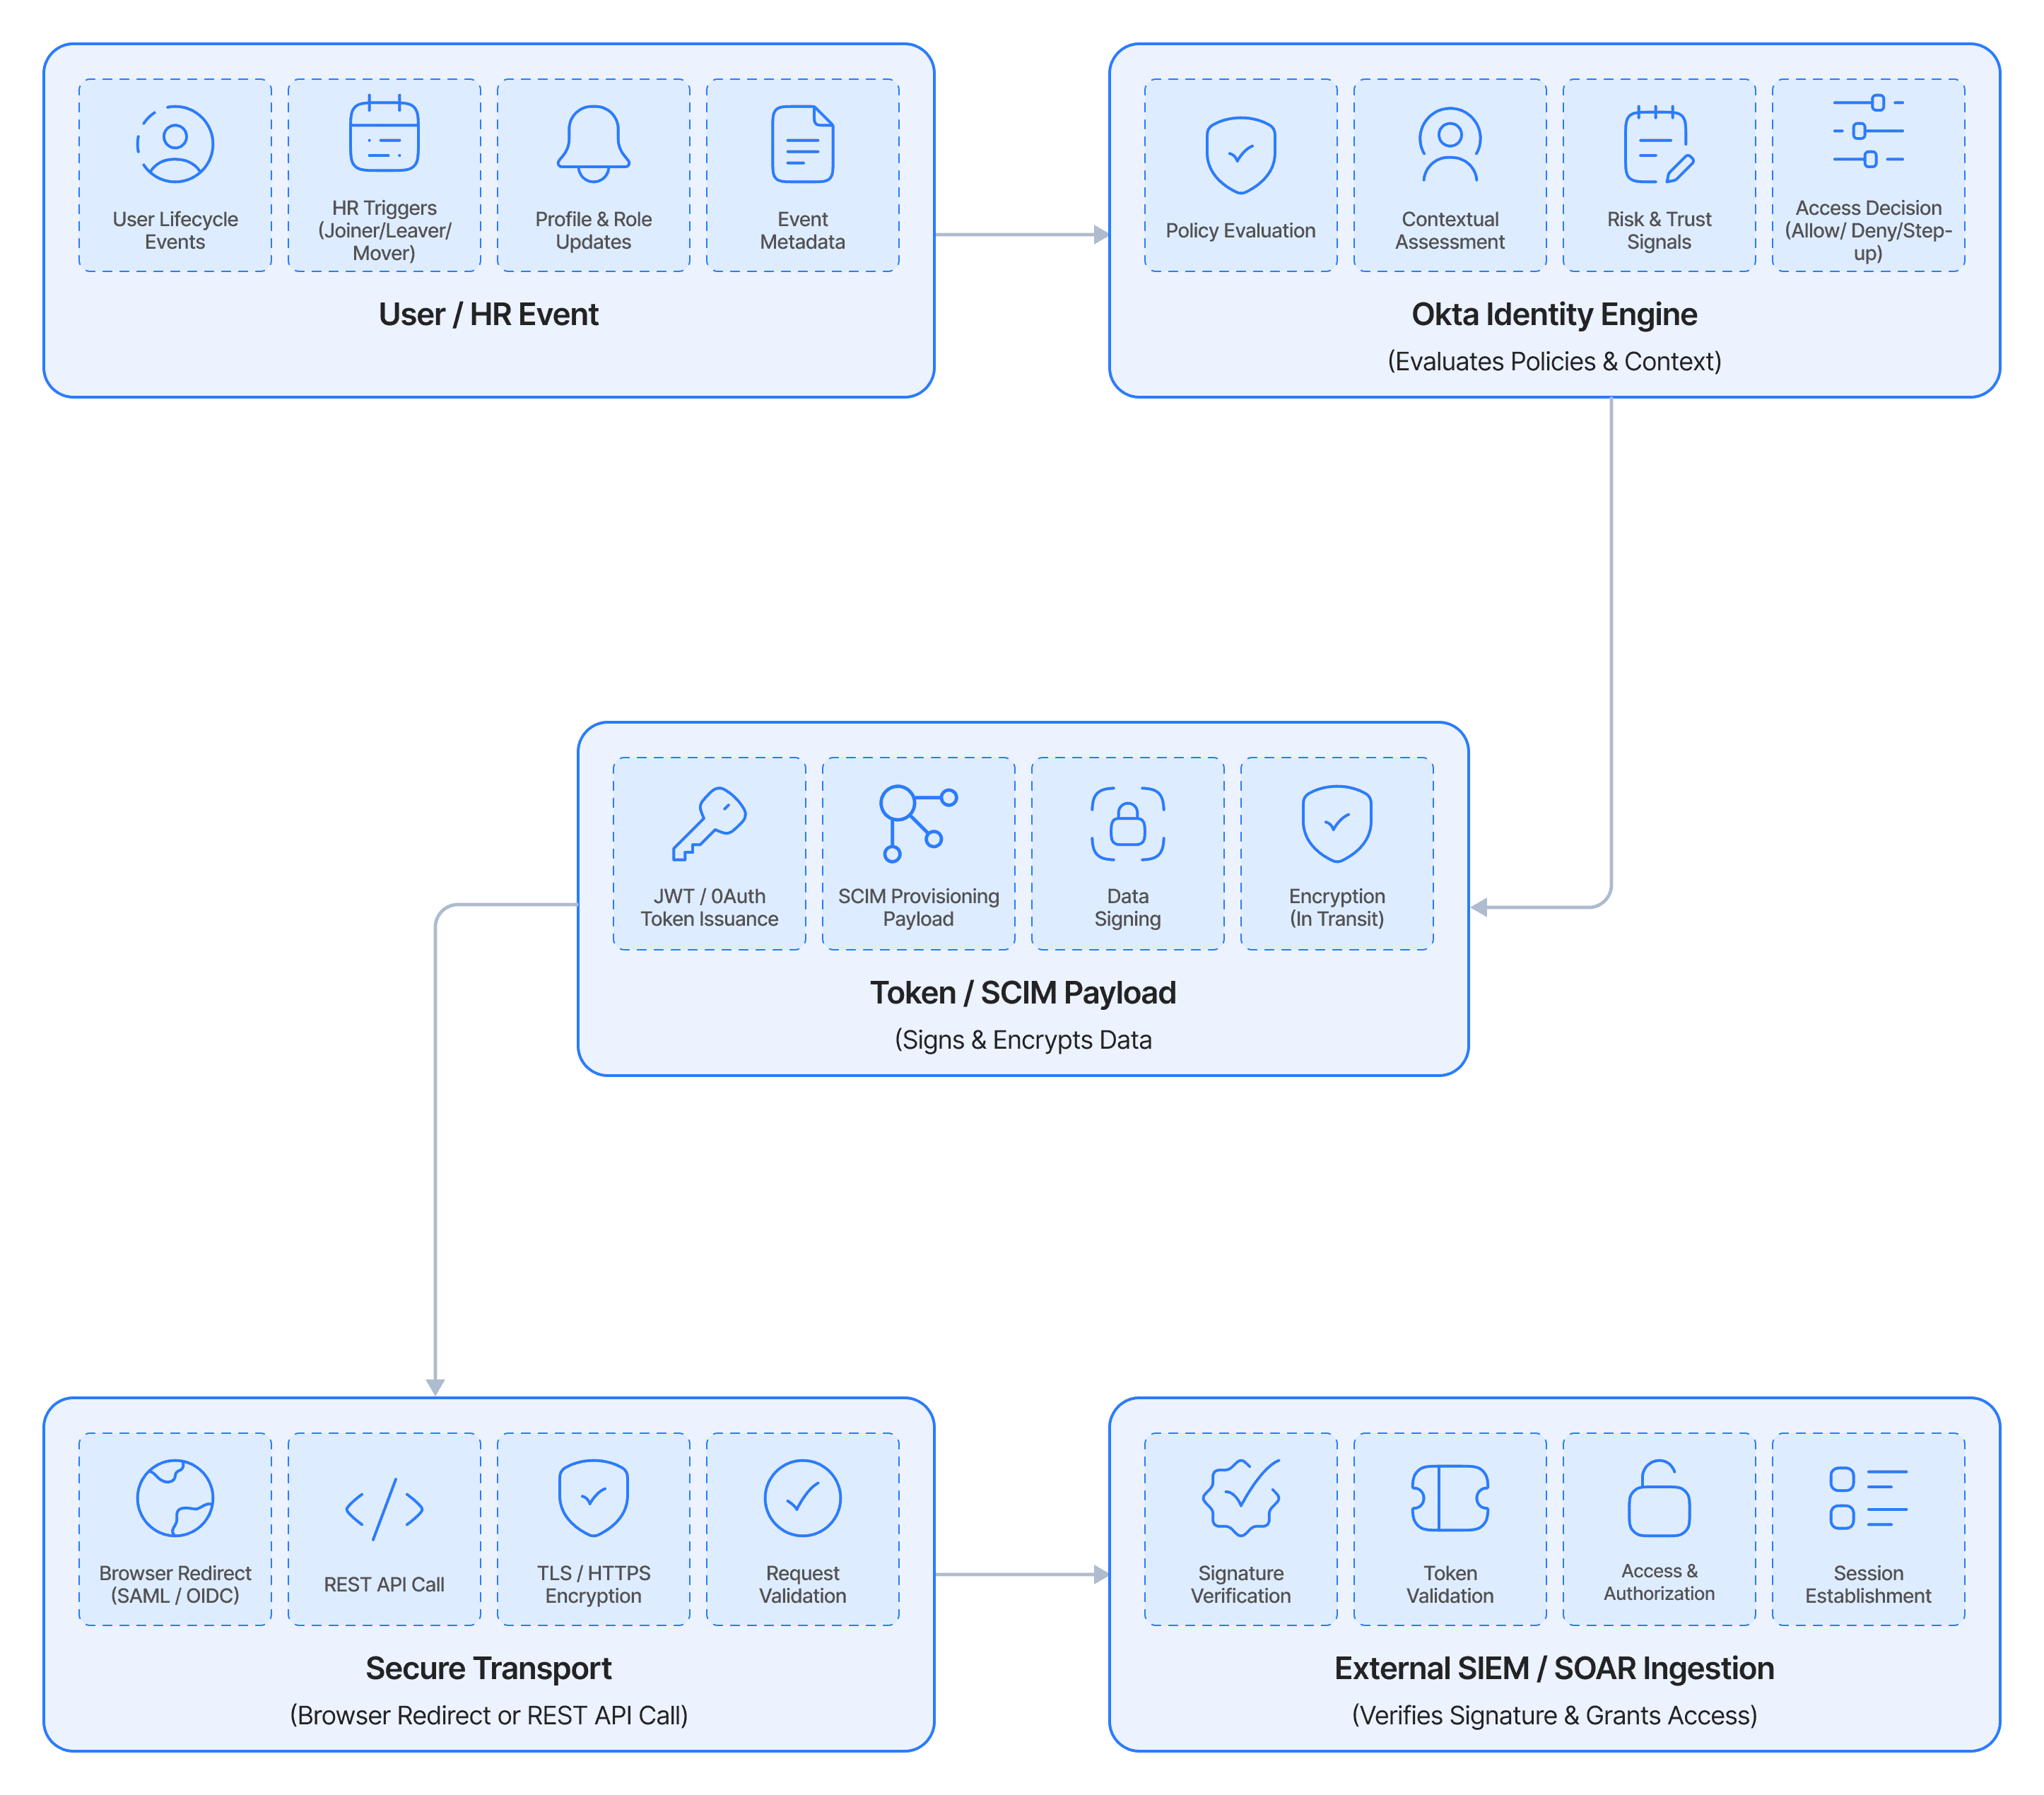
Data flows between the central identity broker and third-party systems to synchronize authentication state and user lifecycle attributes. When an administration change or user login event triggers a request, the platform packages identity details into cryptographically signed tokens or payload bundles and securely delivers them to your destination application's endpoints.
Streamlined Logic
1. Trigger Event: A user attempts to log in to an application, or an administrator updates a user's profile status within the directory source.
2. Token & Payload Generation: The platform evaluates context-aware security policies and generates cryptographically signed assertions (SAML), identity tokens (OIDC), or standard SCIM payloads.
3. Secure Redirection/Delivery: The browser securely performs a redirection dance or the backend issues structured REST API calls to pass credentials and user attributes downstream.
4. Validation & Mapping: The target third-party application validates the digital signature against trusted certificates, unpacks the attributes, and maps user permissions accordingly.
5. Session/Account Modification: The system creates the user session or modifies database permissions, completing the access loop without exposing raw password data.
Okta Integration Benefits
Single Sign-On (SSO)
Bridges your software applications using industry-standard federated protocols like OpenID Connect (OIDC) and SAML 2.0. It provides your users with seamless, single-credential dashboard logins while removing the risks of password reuse.
Lifecycle Provisioning (SCIM)
Automates user provisioning and deprovisioning through the System for Cross-domain Identity Management standard. It tracks modifications made in your identity directory and automatically maps corresponding CRUD actions to downstream applications.
API Service Integrations
Grants secure, machine-to-machine access to the Core Okta API using the OAuth 2.0 client credentials grant. It allows your external scripts, microservices, and backend daemons to interact with identity data securely without any user intervention.
Workflows Connector Builder
Operates as a low-code or no-code platform to build custom logic flows. It builds bespoke operational steps and API integration cards to connect to specialized niche services that lack native catalog integrations.
Integration Use Cases
Automated Workforce Onboarding
Accelerate time-to-productivity for new employees by eliminating manual account creation. We integrate your HR systems directly with identity directories to provision critical applications, assign groups, and grant secure access permissions the moment an employment contract begins.
Phishing-Resistant Single Sign-On
Safeguard corporate assets against advanced credential theft by routing logins through centralized, modern protocols. We replace legacy, weak sign-in forms with phishing-resistant authentication steps and seamless application dashboard tiles.
Instant Universal Deprovisioning
Minimize security exposure from orphaned accounts when employees leave your organization. We instantly trigger deprovisioning alerts that invalidate active sessions, revoke OAuth tokens, and disable accounts across all connected SaaS platforms simultaneously.
Similar Connectors