Strengthen Risk Visibility Across Your Enterprise with Qualys
Overview
Qualys helps organizations continuously discover assets, manage vulnerabilities, and prioritize cyber risk across their environments. By integrating Qualys with ITSM, SIEM, security operations, and CI/CD tools, we help synchronize asset data, streamline remediation, and automate security workflows.
Key Products
Qualys VMDR (Vulnerability Management, Detection & Response)
Provides continuous discovery of all network assets, real-time vulnerability scanning, risk-based TruRisk scoring, and automated patch execution.
CyberSecurity Asset Management (CSAM)
Automatically discovers, categorizes, and inventories all IT, cloud, IoT, and container assets across hybrid environments to eliminate blind spots.
TotalCloud (CNAPP)
Delivers cloud-native application protection by combining CSPM, CWPP, and container security into a single pane of glass for multi-cloud infrastructures.
TruRisk Eliminate / Patch Management (PM)
Correlates vulnerability data with available vendor patches to automate targeted remediation without interrupting production workflows.
TotalAppSec & Web Application Scanning (WAS)
Continuously scans web applications and API endpoints in production and CI/CD pipelines to detect DAST vulnerabilities and logic flaws.

Policy Audit & Compliance (PC)
Evaluates asset configurations against industry benchmarks such as CIS and HIPAA to maintain continuous compliance across global infrastructure.
Qualys Integration Architecture
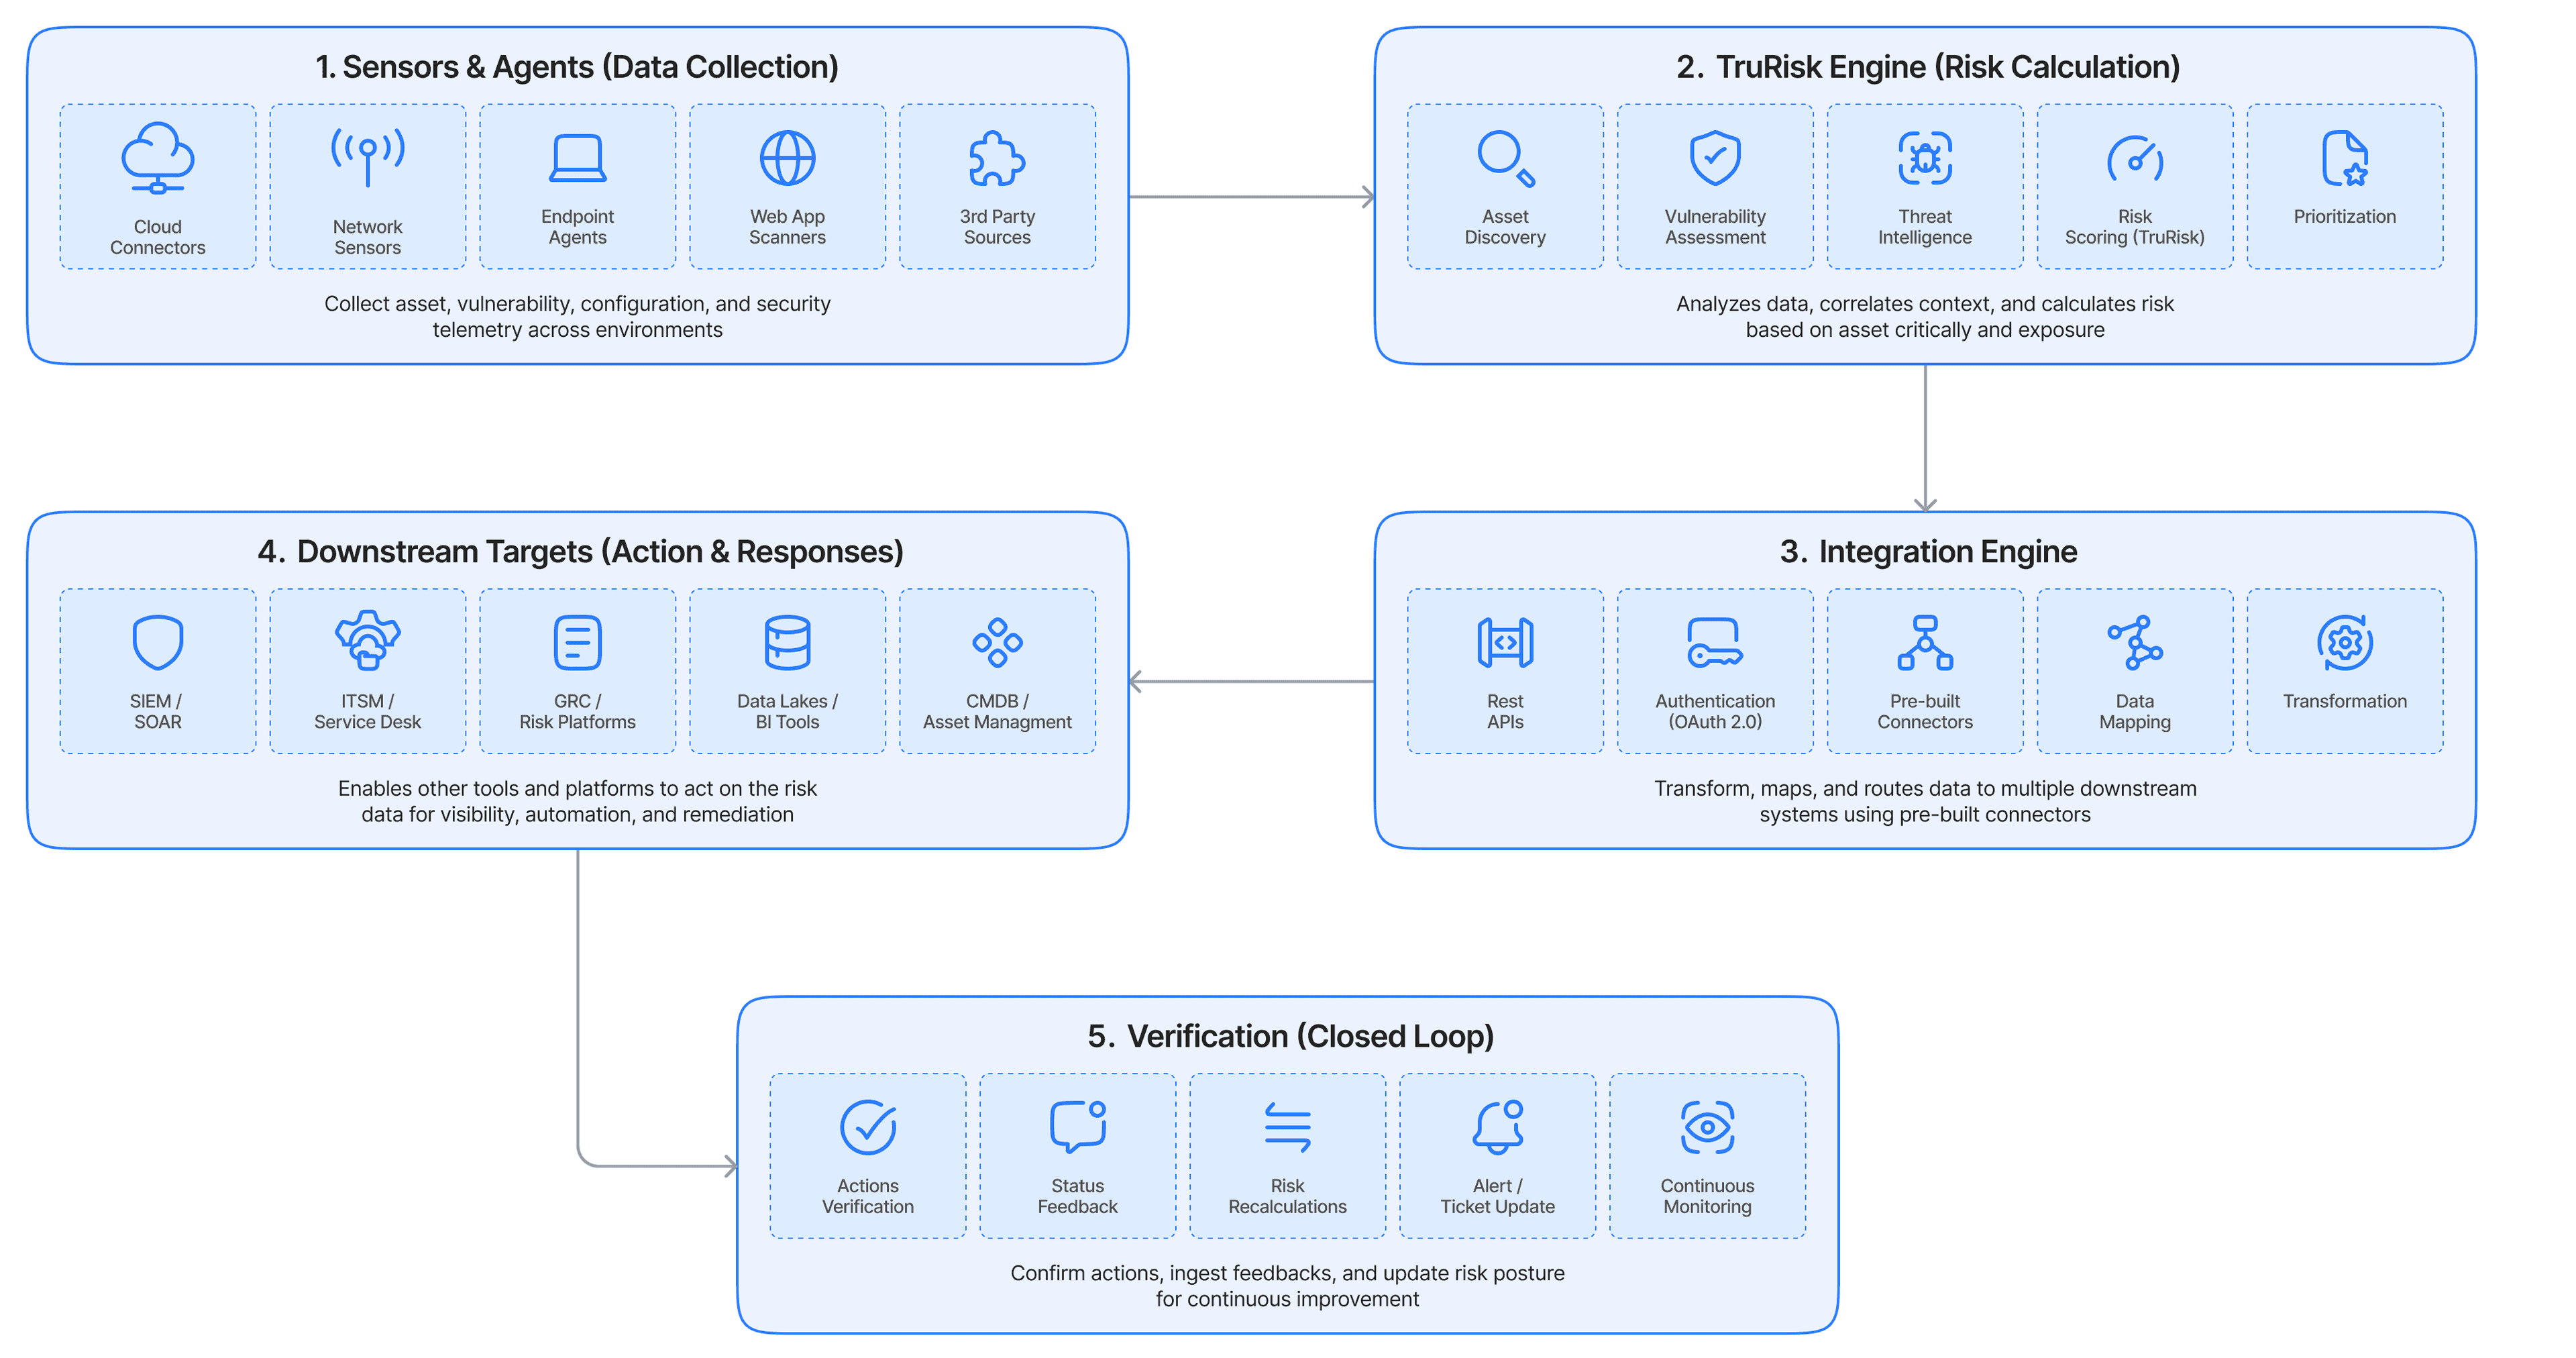
Data flows continuously from target infrastructures into the Qualys Cloud Platform through distributed sensors and Cloud Agents. We configure two-way synchronization engines: Qualys normalizes, indexes, and calculates risk scores, then pushes enriched vulnerability data into external ticketing and SIEM engines. Conversely, actions taken in external ITSM platforms pass back to Qualys to trigger re-scans and verify patch deployment.
Streamlined Logic
1. Ingest & Discover: Cloud Agents and network sensors collect real-time asset configurations, software manifests, and active exposures.
2. Prioritize & Score: The Qualys TruRisk engine correlates vulnerability severity with active threat intelligence and business context to assign a prioritized risk score.
3. Enrich & Translate: Custom middleware or API integration transforms Qualys findings into normalized JSON/REST payloads enriched with CMDB owner mapping.
4. Trigger Workflow: Integrations automatically create prioritized ITSM tickets (e.g., Jira or ServiceNow) or push high-fidelity alerts to a SIEM/SOAR platform.
5. Remediate & Verify: IT teams apply patches or automated remediation scripts; a lightweight re-scan automatically closes the issue in both Qualys and the external ticketing system.
Qualys Integration Benefits
Qualys REST APIs & OpenAPI
Programmatic access for bi-directional data exchange, enabling automated scan triggering, raw asset extraction, vulnerability tracking, and dynamic report generation.
Qualys ROC & Cloud Connectors
Out-of-the-box native connectors that pull cloud metadata and third-party security findings into the Qualys Risk Operations Center for consolidated TruRisk scoring.
Qualys Cloud Agent & Sensor Telemetry
Lightweight agent framework that streams continuous asset and posture metadata directly from endpoints, cloud instances, and containers.
Bulk Stream Ingestion & Export Pipelines
High-throughput export integrations using AWS S3, Azure Blob Storage, or SIEM stream adapters (e.g., Splunk, Sentinel) for raw event correlation.
Integration Use Cases
Dynamic CMDB Bi-Directional Asset Sync
By continuously mapping Qualys CSAM discoveries against enterprise CMDBs like ServiceNow or BMC Helix, we keep your asset inventory accurate. Newly discovered cloud assets or unmanaged endpoints immediately receive appropriate risk profiles and monitoring coverage.
High-Throughput SIEM & Lakehouse Data Streaming
We build performant streaming pipelines that push raw vulnerability detections and security posture events into platforms like Splunk, Microsoft Sentinel, or Snowflake. This enables SOC analysts to correlate Qualys risk metrics with real-time runtime log data.
Shift-Left CI/CD Security Gates
Integrate Qualys Container Security and Web Application Scanning directly into GitHub Actions, GitLab CI, or Jenkins pipelines. Build steps automatically trigger code and container image scans, blocking deployments if critical vulnerabilities breach defined security policies.
Similar Connectors